Artica SIEM for FortiGate
Turn the traffic logs your FortiGate already sends into an inventory of internal devices, destinations and firewall policies, with their traffic over time. Free in the Community Edition.
Artica SIEM reads the traffic logs your FortiGate already sends over syslog. It shows which internal devices used the network, where their traffic went, which firewall policy let it through, and how much data moved, from the last 15 minutes up to 90 days.
The FortiGate pages are free in the Artica Community Edition.
Install from the ISO | Connect a FortiGate | General data | FortiGate status | Clients | Destinations | Policies | How the figures are computed
What you get
- An inventory of the devices behind each FortiGate, built from the logs alone:
MAC address, host name, operating system and vendor when the FortiGate knows them, and the data each device downloaded and uploaded. - The same traffic read from the other side.
For any destination you see which machines talk to it and when the largest transfers happened. - Traffic, log lines and denials for each FortiGate policy, Internet sources included, so you can check that a rule actually fires.
- Downloads, uploads and sessions per tenant over 15 minutes to 90 days, on one page.
- Click any name in a chart legend to open its details, and keep drilling down from there.
Each new window opens on top of the previous one. - Several customers or sites on one appliance.
Every view can be narrowed to a tenant or to one FortiGate. - The Artica AI assistant reads the same data, so you can ask it which policy refused the most traffic this week.
Nothing is installed on the FortiGate.
It keeps sending standard syslog, and the logs stay on your own appliance.
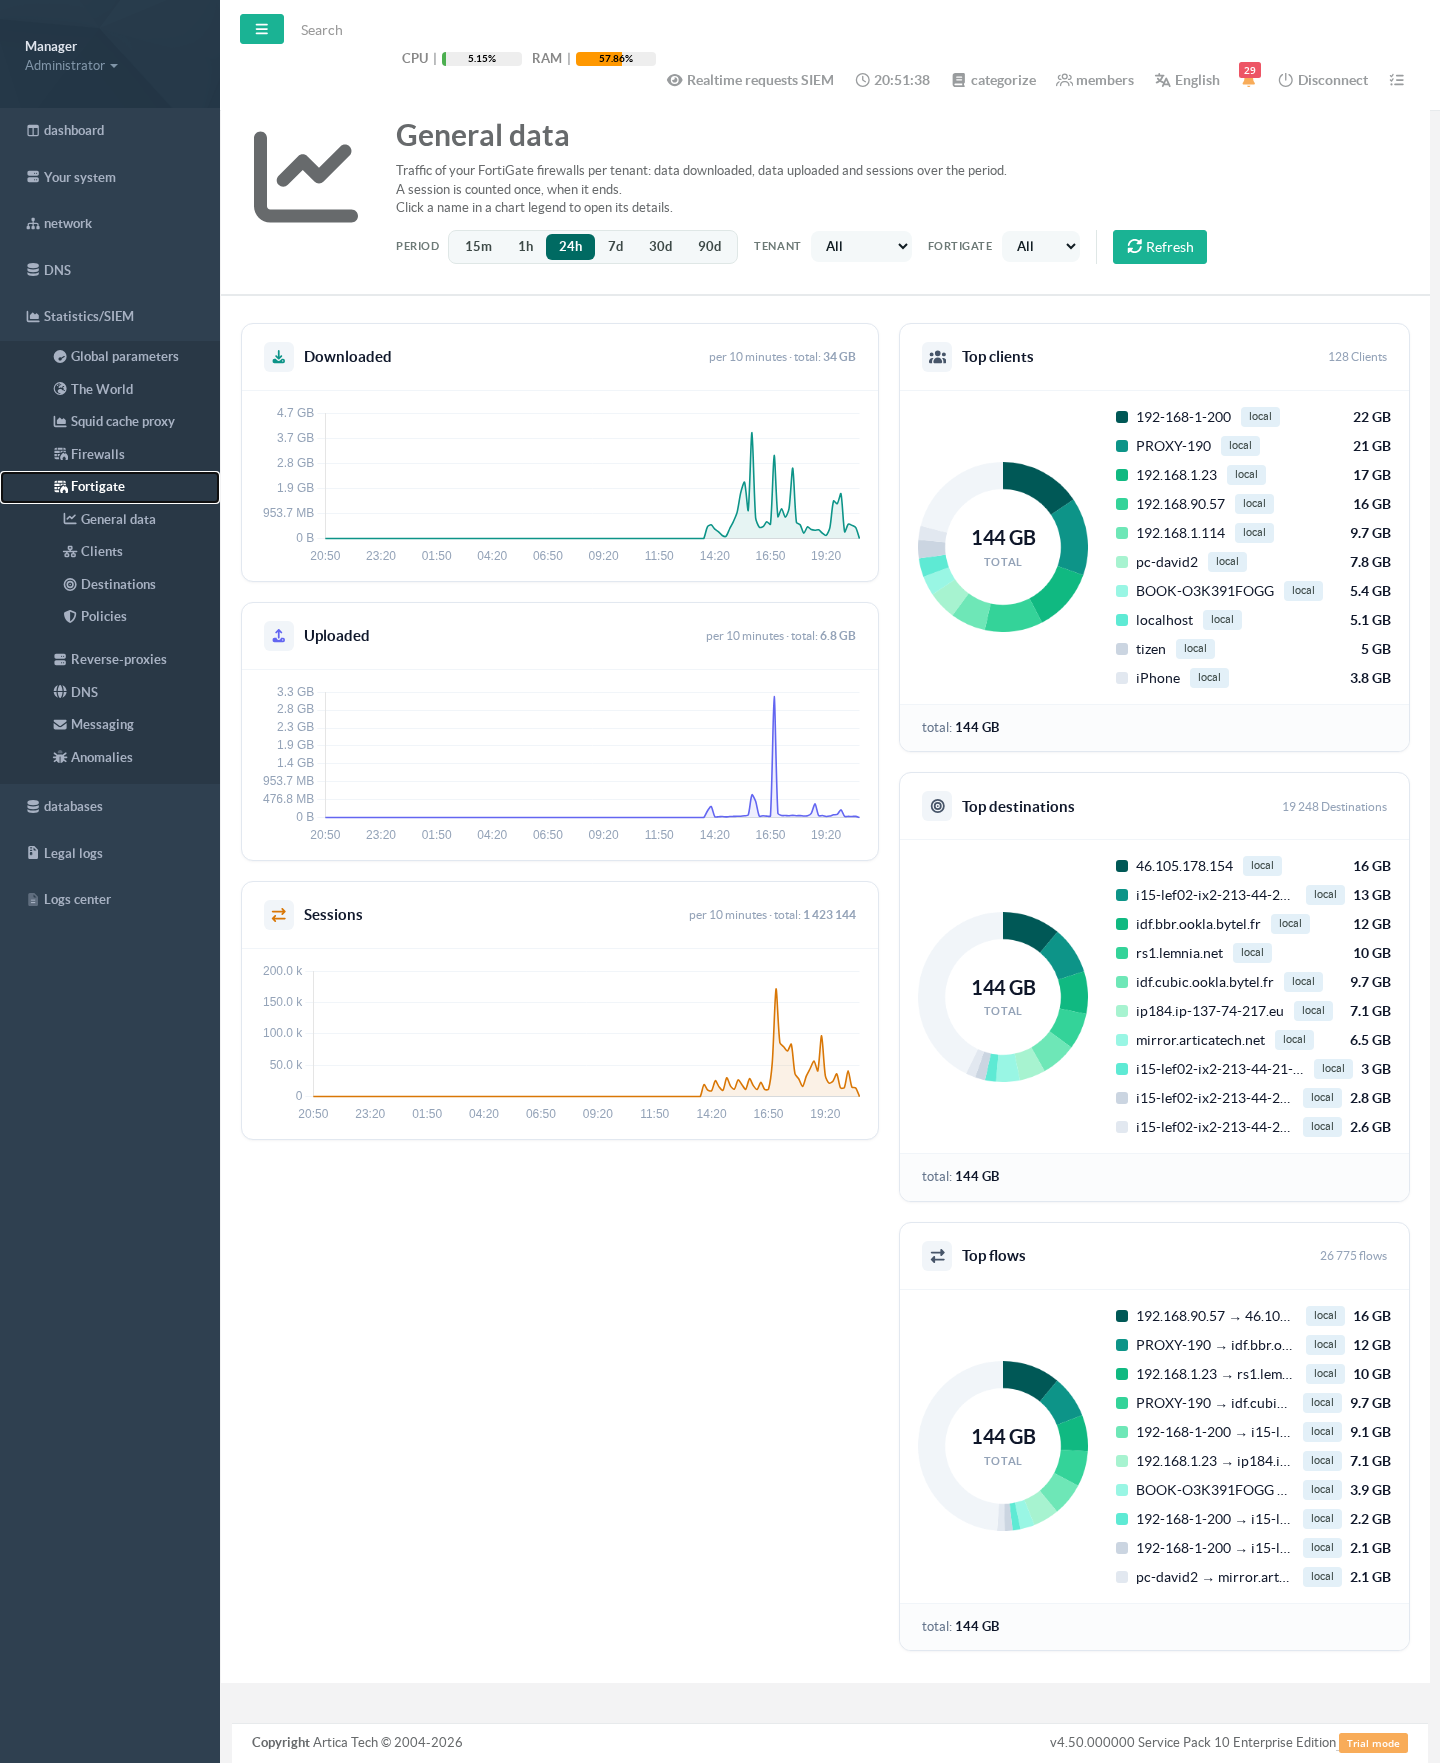
General data: traffic and sessions on the left, top clients, destinations and flows on the right.
Where to find it
In the Artica console, open Statistics/SIEM. The Fortigate entry appears there as soon as the SIEM holds FortiGate data for your account. Clicking it opens the FortiGate status page, and its sub-menu leads to General data, Clients, Destinations and Policies.
Pages in this section
- Install from the ISO:
A new Artica SIEM appliance from the Artica 4.50 ISO image. - Connect a FortiGate:
The syslog settings on the FortiGate and the source declaration on the SIEM. - General data:
Traffic and sessions per tenant, with the top clients, destinations and flows. - FortiGate status:
Policies, applications, UTM actions and interface roles seen in the recent logs. - Clients:
The internal devices and their traffic. - Destinations:
The sites and addresses those devices reach. - Policies:
The traffic and denials of each firewall policy. - How the figures are computed:
Byte counters, sessions, retention and what each figure means.
Requirements
- A FortiGate that can reach the appliance on port 514 (UDP or TCP).
- Sizing: see Prerequisites.