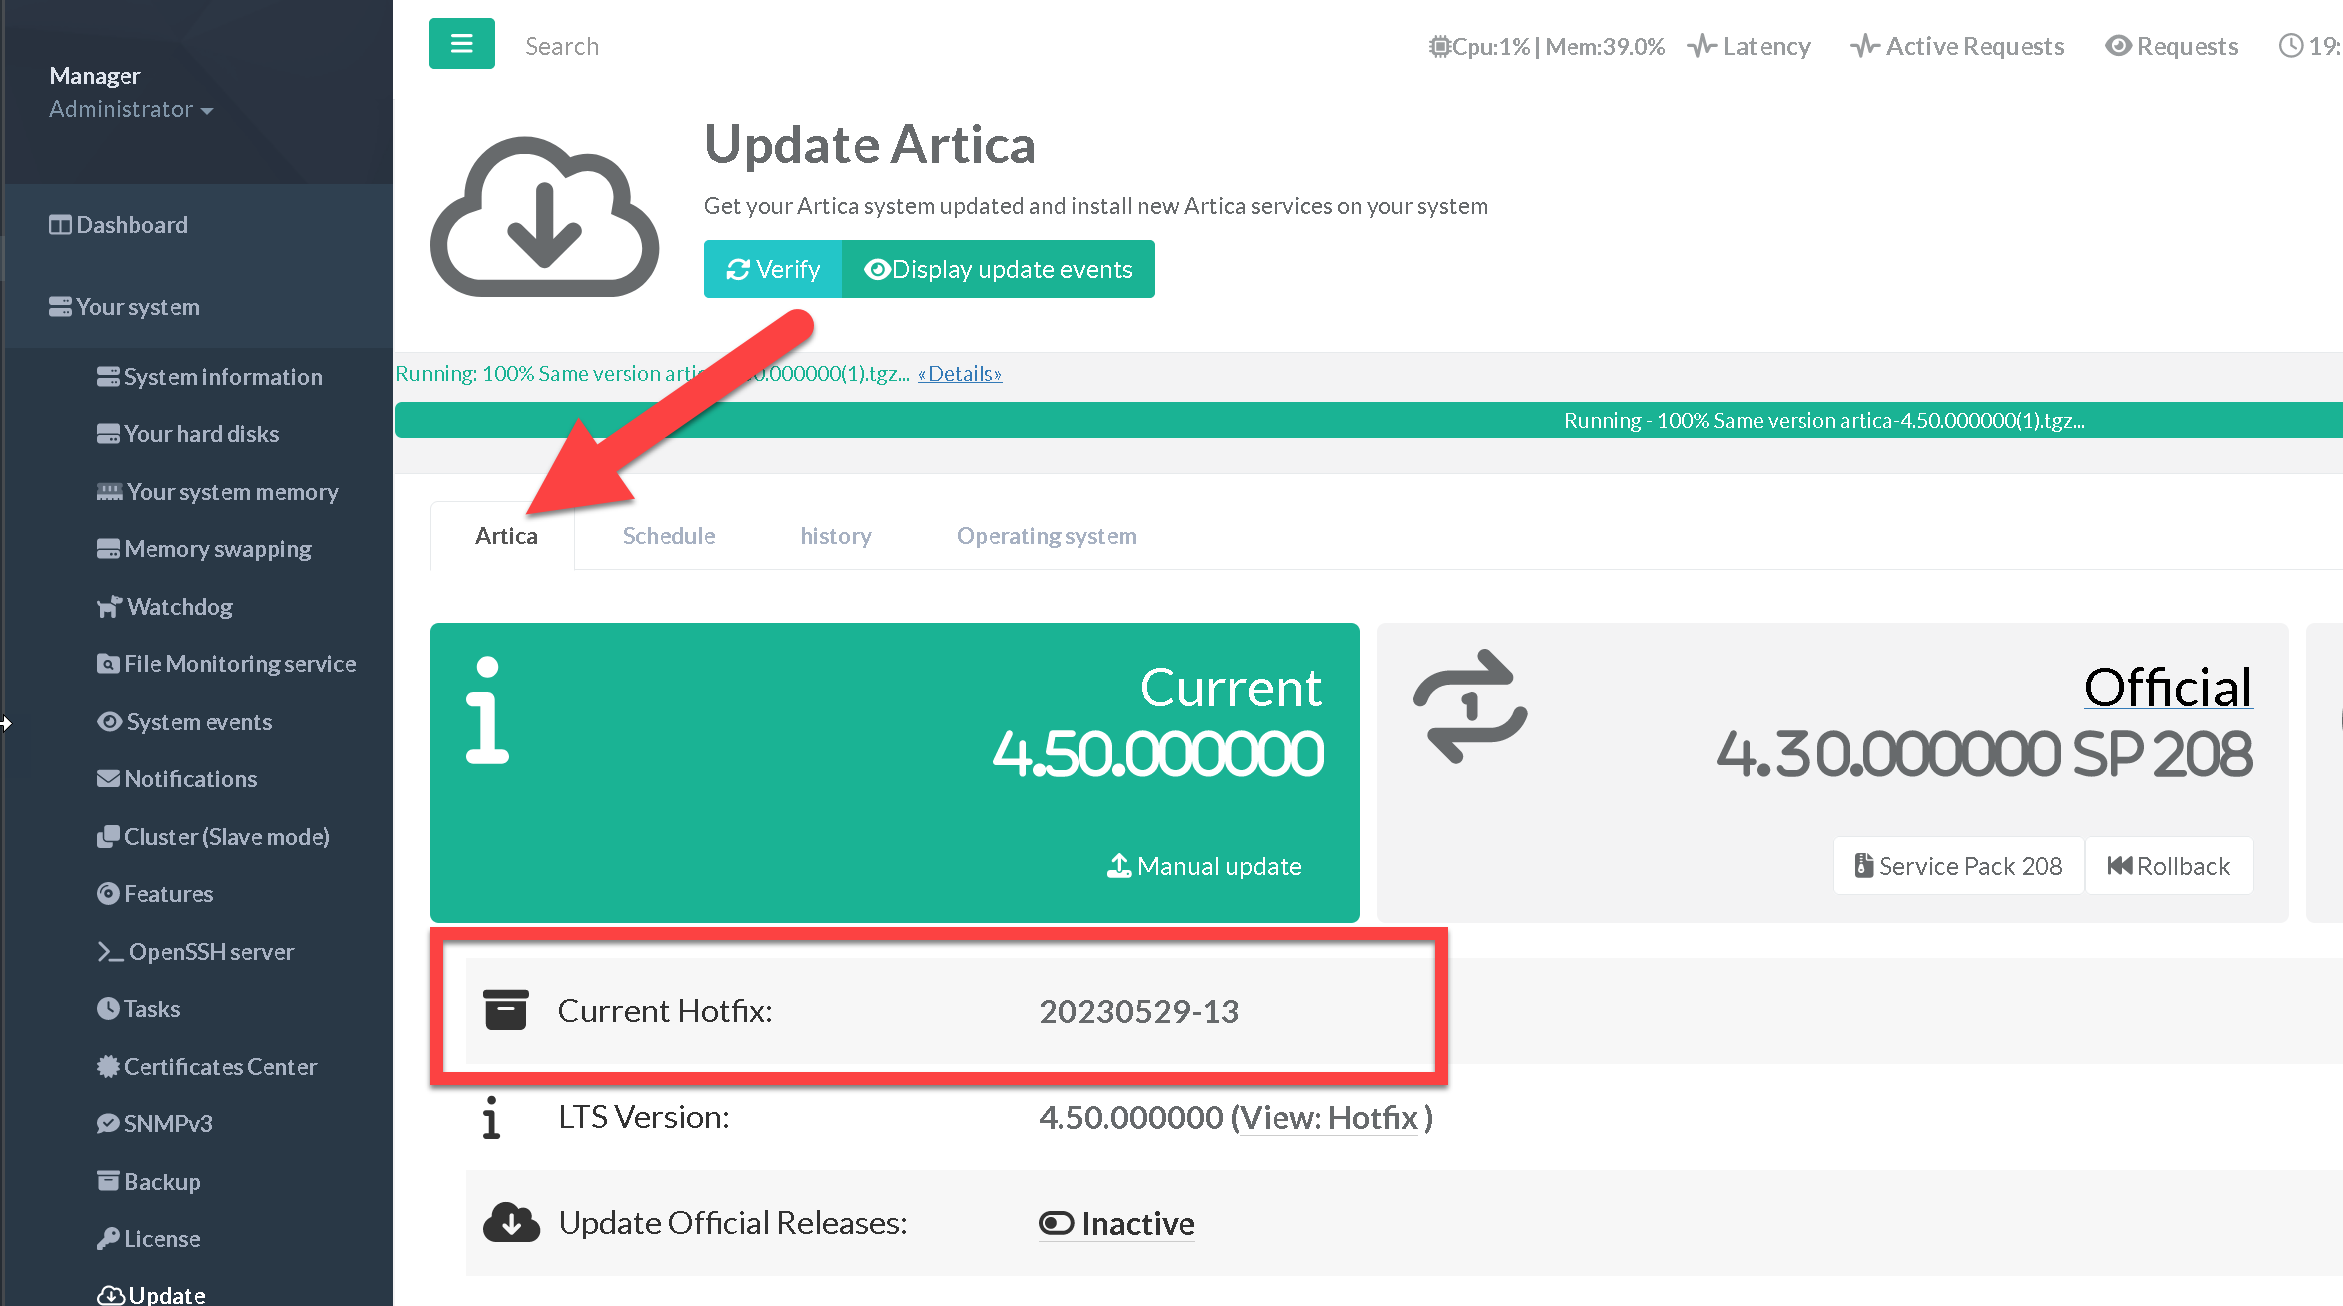
The HotFix generates an error when manually updating the Artica version, it is normal.
It can be applied only for Artica 4.50.00000 Service Pack 10
New Hotfix erase modifications of old applied HotFixes.
¶ Official Hotfix
¶ Issues resolved by The Hotfix
- 20261023-17: Fix: in Artica, The network interface page now shows TCP/IP checksum offloading as always on for VMware vmxnet3 and virtio network cards instead of offering a switch that the system would not apply.
- 20261023-17: Add: in Artica, At startup, servers already installed on VMware vmxnet3 or virtio network cards switch their network offloads back on when an earlier configuration had turned them off.
- 20261023-17: Fix: in Artica, Applying the network configuration no longer disables TCP segmentation, scatter-gather and receive offloads on virtual network cards: they are now always switched on for VMware vmxnet3 and virtio cards and left to the driver on Hyper-V and Xen, which restores full network speed on virtual appliances.
- 20261023-17: Fix: in Artica, The Artica REST API service is no longer reported as failed when the system stops another process for lack of memory, and a service state left failed that way is repaired automatically.
- 20261023-17: Fix: in Artica Proxy, The category service started by Artica now runs in its own system unit or scope, so a memory kill of it no longer affects the Artica REST API service.
- 20261023-17: Fix: in Artica Proxy, A categories server now republishes its databases and its categories table to the proxies as soon as the web-filtering repository is enabled, instead of reporting the table as unavailable until a category is recompiled.
- 20261023-17: Add: in Artica DNS, The new DNS record dialog shows one tile per record type, with a short explanation of each type and a search box, instead of a drop-down list.
- 20261023-17: Fix: in Artica Proxy, The category service no longer rebuilds its table of category names for each request, which reduces its memory use.
- 20261023-17: Fix: in Artica, The DNS Firewall cache can no longer be sized beyond what the server memory can hold: all DNS caches together are kept under 70% of the RAM.
- 20261023-17: Fix: in Artica, Archived logs copied to another disk are now removed after the retention period counted from their archive date, not from the date of the copy.
- 20261023-17: Fix: in Artica, Archives left in the former backup directory are removed once an identical copy exists in the configured backup directory, which frees the system disk.
- 20261023-17: Fix: in Artica, A single failed system unit no longer makes Artica start every other service outside systemd.
- 20261023-17: Fix: in Artica Proxy, The PAC server started outside its system unit is now restarted under it automatically, so the unit no longer stays in the failed state.
- 20261023-17: Fix: in Artica, The DNS Firewall service no longer leaves defunct dnsdist processes behind each time dnsdist stops, and no longer keeps its console output in the Artica API memory.
- 20261023-17: Fix: in Artica, The left menu no longer keeps every visited entry highlighted in white: only the entry of the page currently displayed stays highlighted.
- 20261023-17: Fix: in Artica, Restarting a stopped Zabbix agent no longer reports a failure while the agent actually starts.
- 20261023-17: Fix: in Artica, Searching the Zabbix agent events no longer passes the search text to a system command, and lists the newest events first.
- 20261023-17: Add: in Artica, The AI assistant can read the last bulk categorization test and, after approval, run it again, export a personal category, and perform the emergency removal of ClamAV.
- 20261023-17: Fix: in Artica, Uploading ClamAV signatures as a zip file no longer needs the unzip command, installs the incremental databases (.cld) too, and fails clearly when the archive holds no signature.
- 20261023-17: Fix: in Artica, The emergency removal of ClamAV now purges only the packages actually installed and refuses to run while another package operation is in progress.
- 20261023-17: Fix: in Artica Web Filtering, Testing a list of websites against the categories is now done by the Artica daemon, accepts URLs and proxy log lines, and no longer builds its result page from unescaped site names.
- 20261023-17: Fix: in Artica Web Filtering, Exporting the websites of a category no longer goes through a system command.
- 20261023-17: Fix: in Artica, The DHCP configuration file is now shown read-only with its DDNS and OMAPI keys masked, and is no longer copied to a folder served by the web console.
- 20261023-17: Add: in Artica, The AI assistant can now search ten service logs and see which parent-proxy rules are applied, and, after approval, apply the AppArmor boot setting and the TFTP server settings, test the FTP account of the console and export the event tables.
- 20261023-17: Fix: in Artica Proxy, The web filtering service no longer uses up to 1 GB of extra memory within a minute when it categorizes many IP addresses, which could make the system stop it or the DNS service on servers with 4 GB of memory.
- 20261023-17: Fix: in Artica Proxy, The IP addresses of Blizzard game servers are now categorized as Games; a typo in the first address range had disabled the whole list.
- 20261023-17: Fix: in Artica, The AppArmor protection switch of the System information page works again: it updates the boot loader instead of leaving its progress bar stuck.
- 20261023-17: Fix: in Artica, Searching the events of a service (Redis, SNMP, Rsync, ITCharter, Wazuh agent, web error page, mail filter, DNS backends, statistics retention, Active Directory API) no longer passes the search text to a system command, and lists the newest events first.
- 20261023-17: Fix: in Artica, Saving the TFTP server settings no longer reinstalls the service each time, and the server listens on all addresses when the chosen interface has none.
- 20261023-17: Fix: in Artica, Exporting a database table to CSV no longer requires the sqlite3 command to be installed.
- 20261023-17: Fix: in KasperskyTIP, The installation ISO no longer stores the root password in clear text; only its hash is written to the installer configuration.
- 20261023-17: Add: in Artica, The AI assistant can read the certificate of a Docker Store application and propose, for approval, the installation of a hardened Vaultwarden server.
- 20261023-17: Add: in Artica, The Docker Store can now install a ready-to-use Vaultwarden password server in one step: HTTPS certificate generated for your host name, public sign-up closed, administration page protected by a hashed token, optional mail server, and a certificate authority to download for the client devices.
- 20261022-17: Fix: in Artica, The Web console PHP engine now loads only the extensions the console uses (about 46 modules instead of 61, without FFI, XML-RPC or Phar), and no longer depends on the extensions enabled by the operating system packages.
- 20261022-17: Fix: in Artica, PHP extensions are no longer loaded twice by the Web console: duplicates are removed when the configuration is written, then checked against PHP itself and disabled if any remain.
- 20261022-17: Fix: in Artica, Two unused PHP-FPM pools with permissive settings were removed, and the PHP engine no longer writes memory dumps of its administrator processes or loads extensions at runtime.
- 20261022-17: Fix: in Artica, The root back-end of the console no longer ships about 1,000 unused request handlers and 35 unused scripts, reducing the code that runs with administrator privileges.
- 20261022-17: Add: in Artica Proxy, ACL objects listing user names go back to the native Squid user list when the installed proxy includes the Artica letter-case fix, and keep the pattern-based match on any other proxy version.
- 20261022-17: Fix: in Artica, Installing a system package from the console now reports a failure when the package could not be installed, instead of always ending with a success.
- 20261022-17: Fix: in Artica, The system checks that follow a Service Pack installation now run again; they called a file that did not exist.
- 20261022-17: Fix: in Artica, The Apply button of the web console no longer fails with "This link has expired or was altered" when several pages load at the same time, for example on the Address Rewriting page after a hotfix update.
- 20261022-17: Add: in Artica AI, The assistant can now check which disk the boot loader will be written to and warns when the next GRUB update could leave the server unable to start.
- 20261022-17: Add: in Artica, The appliance now warns when the boot loader is configured for the wrong disk, including on VMware, and apt displays a warning before a system update would leave the server unable to restart.
- 20261022-17: Add: in Artica, A watchdog now closes forgotten idle statistics database connections before the connection limit is reached, and names the program that opens too many of them.
- 20261022-17: Fix: in Artica, The statistics database now closes sessions left idle for 15 minutes and reports session states again, which lets idle connections be cleaned up automatically.
- 20261022-17: Fix: in Artica Proxy, Updating the proxy logging helper no longer leaves a moment where the helper is missing, which made a proxy reload fail during Artica updates.
- 20261022-17: Fix: in Artica Proxy, Blocking rules restricted to plain HTTP no longer make the new configuration be refused right after an Artica update.
- 20261022-17: Fix: in Artica, A reboot no longer leaves the Motorcomm YT6801 network card armed for Wake-on-LAN; wake-up stays enabled only after a power-off.
- 20261022-17: Fix: in Artica Proxy, ACL objects of type "Is Authenticated" now match any authenticated user instead of being checked as an Active Directory group of the same name, which matched nobody.
- 20261022-17: Add: in KasperskyTIP, Blocklists are saved to disk after each update and reloaded at startup, so the data port serves the last known lists immediately after a restart.
- 20261022-17: Add: in Artica SIEM, New DHCP pages show requests, leases and a dashboard, and the address sheet now lists the DHCP leases of an address.
- 20261022-17: Add: in Artica, On Debian 10, the System information page warns when PHP is exposed to PHP2Shell (CVE-2026-109618, CVE-2026-109619) and offers a button that installs the fixed PHP 7.3 from the Freexian Extended LTS repository, then restarts PHP.
- 20261022-17: Fix: in Artica, Two nodes that each declare the other as their cluster master no longer make Meta send a policy back and forth between them every three minutes; the policy is held and the editor explains why.
- 20261022-17: Add: in Artica, The delivery status of a Meta policy now lists the cluster slaves reached through their master and flags those whose master is not managed by Meta.
- 20261022-17: Add: in Artica, The AI assistant can now list Meta policies, check their delivery to each node and apply, attach or detach them with confirmation.
- 20261022-17: Add: in Artica, The Meta console can define virtual network cards and map each one to the real interface of every node, and the old per-group proxy page is replaced by the Policies page.
- 20261022-17: Add: in Artica, The Meta console has a policy editor: each proxy setting can be left to the node or defined by the policy, with the Artica default shown for reference, plus the general whitelist and blacklist, the targeted nodes and groups, and the delivery report of every node.
- 20261022-17: Add: in Artica, The Meta console now has a Policies page to create named sets of proxy settings and apply them to nodes and groups of nodes, with the update status of each policy.
- 20261022-17: Add: in Artica Proxy, The Certificate Center can now remove root authorities from the system trust store and refuse specific compromised certificates, and the change is replicated to every proxy of the cluster.
- 20261022-17: Add: in Artica, The AI assistant can read the system trust store and, with an administrator's approval, remove or restore trusted roots, add authorities, refuse a compromised certificate and apply the policy.
- 20261022-17: Fix: in Artica Meta, Opening the web console of a managed server through the Meta console no longer logs the administrator out of the Meta console.
- 20261022-17: Fix: in Artica Meta, Opening the web console of a managed Artica server through the Meta console no longer returns a 404 error on servers where the Artica AI remote terminal verifier is configured.
- 20261022-17: Add: in Artica, The network agent status page now shows the state of the tunnel to the Meta server when the agent is enrolled in reverse mode, and its status tiles all have the same height.
- 20261022-17: Fix: in Artica, A failed enrollment with the Meta server no longer keeps any data from the enrollment file on the agent, and an earlier unfinished enrollment no longer blocks a new enrollment file.
- 20261022-17: Fix: in Artica, Enrollment failures with the Meta server now show their real cause instead of always reporting a certificate error.
- 20261022-01: Fix: in Artica, Installing a hotfix no longer breaks the connection point used by agents to enroll with the Meta server, which made every enrollment fail with a 502 error.
- 20261022-01: Fix: in Artica, Enrolling an agent with a Meta server from the enrollment file no longer fails with a certificate error when "Allow self-signed certificates" is checked and the Meta server uses a publicly trusted certificate.
- 20261022-01: Fix: in Artica Proxy, A web-filtering category with no name no longer turns every official category into "Unknown" in the filtering rules.
- 20261022-01: Add: in Artica, The DNS records page shows whether each record is actually served by the DNS cache, its TTL, and can filter by record type.
- 20261022-01: Add: in Artica, The DNS cache can stop answering IPv6 (AAAA) records, for every domain or for a list of domains, without emptying the cache.
- 20261022-01: Add: in Artica, Each DNS firewall policy (RPZ) can limit the size and duration of its list download, so an oversized or slow source can no longer exhaust memory or stall the update.
- 20261022-01: Fix: in Artica, Adding an Active Directory DNS record no longer empties the DNS cache.
- 20261022-01: Fix: in Artica, Editing a local DNS record no longer rebuilds the DNS firewall zones, which could restart the DNS cache.
- 20261022-01: Fix: in Artica, Deleting one DNS record of a host no longer stops the DNS cache from answering the other records of that host.
- 20261022-01: Add: in Artica, The disk details now offer a "Format disk" button on a disk with no mounted partition: after a warning, it erases every partition and creates a single unmounted ext4 partition.
- 20261022-01: Fix: in Artica, The DHCP install button of the dashboard no longer fails with a "404 Not found" error.
- 20261022-01: Add: in Artica, On a physical server without smartmontools, the disk details and the SMART monitoring page offer an "Install SMART" button with an installation progress bar.
- 20261022-01: Fix: in Artica, The installer no longer offers disks smaller than 10 GB, which are too small to hold an Artica system.
- 20261022-01: Fix: in Artica, The installer now recognizes the internal SD modules of servers, such as the Dell Internal Dual SD, and offers them as installation disks instead of treating them as external USB keys.
- 20261022-01: Fix: in Artica, The cache rate and queries tiles of the DNS cache service show the real counters again instead of staying at 0.
- 20261022-01: Add: in Artica, The PostgreSQL status page now says when the database service is disabled and offers an "Enable PostgreSQL" button that enables and installs it.
- 20261022-01: Fix: in Artica, After the system clock is corrected backwards at boot, the scheduled maintenance tasks resume at once instead of stopping for as long as the correction.
- 20261022-01: Fix: in Artica, After the system clock is corrected backwards, the service status pages no longer show an outdated state for as long as the correction.
- 20261022-01: Fix: in Artica, A freshly installed DNS cache service answers on the network interfaces right away instead of listening on the loopback only.
- 20261022-01: Fix: in Artica, The DHCP configuration, leases and reservations pages no longer fail with an internal error when the PostgreSQL service is not running.
- 20261022-01: Fix: in Artica Reverse Proxy, The maintenance mode switch is back in the web services list (action menu of each website) and in the settings of each website.
- 20261022-01: Fix: in Artica Reverse Proxy, "Compile your rules" in the Web Application Firewall rules no longer fails with an error on appliances where GeoIP is enabled, so custom firewall rules are applied again.
- 20261022-01: Fix: in Artica Proxy, When the disk holding the system logs stops responding, the reverse-proxy service keeps running and only loses log lines instead of freezing until the disk recovers.
- 20261022-01: Fix: in Artica Proxy, The web application firewall audit index is no longer written to the system logs disk, so a stalled logs disk no longer stops the reverse-proxy from serving websites.
- 20261022-01: Add: in Artica AI, The assistant can read whether the Web console client-certificate authentication is enabled and really enforced, the state of the console certificate authority and which accounts hold a certificate.
- 20261022-01: Fix: in Artica, Web console client certificates are no longer stored in a public folder of the web server, and the password chosen for a certificate is no longer saved in the settings.
- 20261022-01: Fix: in Artica, The "Authenticate SSL Clients" option of the web console is now enforced by the web server: browsers without a client certificate issued by the console are refused before reaching the login page.
- 20261022-01: Fix: in Artica, The PHP configuration of the web console and of published PHP sites now applies the recommended mitigation for the PHP2Shell remote code execution flaws (CVE-2026-109618, CVE-2026-109619) until patched PHP versions are installed.
- 20261022-01: Fix: in Artica, Removing an OpenVPN client connection now also removes its watchdog entry, so the deleted tunnel is no longer restarted automatically.
- 20261022-01: Fix: in Artica, A load-balancer used as the DNS server of its proxy farm now answers DNS on its failover virtual IP, so member proxies no longer lose name resolution and Internet access when they point to that address.
- 20261022-01: Fix: in Artica, The installer now wipes old LVM volumes, RAID metadata and partition tables from the target disk before partitioning, so a disk that held a previous installation no longer stops the setup.
- 20261022-01: Fix: in Artica, The installer now removes the Artica labels left on other disks by an older installation, so the machine can no longer boot the old system after the first restart.
- 20261022-01: Add: in Artica, External USB disks are no longer offered anywhere during the installation, including manual partitioning and boot loader selection.
- 20261022-01: Fix: in Artica Proxy, Strict deny rules edited on the master of a proxy cluster are now replicated to the other members again; until now they stayed on the master.
- 20261022-01: Add: in Artica SIEM, The firewall events can now be searched by source MAC address, written in any common form and optionally followed by a destination port.
- 20261022-01: Fix: in Artica SIEM, Filtering firewall events by MAC address is now refused to accounts that are not allowed to see MAC addresses, which could otherwise check whether a hidden address was on the network.
- 20261022-01: Fix: in Artica Proxy, ACL objects listing user names now match a member whatever the letter case of the login, where Squid 6 and later only recognized logins written entirely in lowercase.
- 20261022-01: Fix: in Artica SIEM, Saving or deleting a firewall source now reports its errors in a translated error message instead of an untranslated line at the top of the form.
- 20261022-01: Fix: in Artica SIEM, The FortiGate menu entry and tab for firewall policies are now named Policies, like their page.
- 20261022-01: Add: in Artica Proxy, The Web-filtering categorization service now always recognizes sites hosted on Cloudflare Pages, Vercel, Wix Studio, GitHub Pages, Webflow, Netlify and Typedream as individual tenants when filing phishing reports.
- 20261022-01: Add: in Artica Proxy, The Web-filtering categorization service now imports the PhishDestroy blocklist into the Phishing category.
- 20261022-01: Fix: in Artica, The SIEM description in the product choice of the installation wizard is now short enough to fit inside its tile.
- 20261022-01: Add: in Artica, The AI assistant can now report how much traffic and how many sessions went through the FortiGate firewalls over a period, for one tenant if needed, and which machines and destinations account for most of it.
- 20261022-01: Add: in Artica SIEM, A new FortiGate General data page shows, per tenant and FortiGate over 15 minutes to 90 days, the data downloaded and uploaded and the number of sessions, next to the top clients, destinations and flows.
- 20261022-01: Add: in Artica SIEM, In every FortiGate chart legend, a client, destination or policy name now opens its details, on top of the window already open.
- 20261022-01: Fix: in Artica SIEM, A FortiGate client whose announced name is only a control character is now shown by its address instead of an unreadable symbol.
- 20261022-01: Add: in Artica SIEM, The event tables (firewall, proxy, web filtering, DNS and web server requests) now show the name of the machine that held the DHCP lease on an address at the time of the event, unless a local host name is already known.
- 20261022-01: Add: in Artica, DHCP requests, leases and reservations are now sent to the SIEM when the appliance serves DHCP and is connected to a SIEM.
- 20261022-01: Add: in Artica, The AI assistant can tell whether the DHCP events reach the SIEM and, after approval, turn them on or off.
- 20261022-01: Add: in Artica, The AI assistant can now tell where the traffic of the machines behind a FortiGate goes, which clients talk to a given destination, and when the biggest transfers happened.
- 20261022-01: Add: in Artica, The AI assistant can now tell which FortiGate policies let the most traffic through or refuse the most, and which clients cross a given policy.
- 20261022-01: Add: in Artica SIEM, A new FortiGate policies page shows the traffic, logs and denials of each firewall policy, Internet sources included, with the top policies, a searchable list and per policy its clients, destinations, largest flows and bandwidth over 1 hour to 21 days.
- 20261022-01: Add: in Artica SIEM, A new FortiGate destinations page shows what internal devices download from and upload to each destination, with the top destinations, a searchable list with trend lines and per destination its clients, largest flows and bandwidth.
- 20261022-01: Add: in Artica, The AI assistant can now show where an internal machine seen by a FortiGate sends and receives the most traffic, and when its biggest transfers happened.
- 20261022-01: Add: in Artica SIEM, Clicking a FortiGate client opens its details: top destinations, largest 10-minute flows, a bandwidth chart per 10 minutes and a searchable list of every destination with data received and sent, over 1 hour to 21 days.
- 20261022-01: Add: in Artica, The AI assistant can now tell when an internal machine seen by a FortiGate used the network, with its peak hours over the last week.
- 20261022-01: Add: in Artica SIEM, The FortiGate client list now shows a 24-hour trend line and a relative bar for received and sent data, the device type, the operating system and whether the device is active, with page navigation.
- 20261022-01: Add: in Artica SIEM, The FortiGate clients statistics now show large rings with the total received or sent in the centre, and each card opens the full ranking of the top 100 clients.
- 20261022-01: Add: in Artica SIEM, The FortiGate status view has a new layout with ranked bars, the share of each value and a link on every card to its full ranking.
- 20261022-01: Add: in Artica SIEM, The first-installation wizard can now set up a SIEM appliance: it downloads ClickHouse from the ArticaTech repository, then installs and enables the SIEM, with progress shown both in the wizard and in the SIEM feature section.
- 20261022-01: Fix: in Artica, Importing a p7r or p7b certificate answer no longer erases the private key of the request it completes, and a certificate that does not match that key is refused.
- 20261022-01: Fix: in Artica, Restoring a certificates database backup now replaces the certificates in a single safe step instead of overwriting the database file in use, and older backups restore correctly.
- 20261022-01: Fix: in Artica, The PFX password is no longer kept in the web session during a certificate import, and PFX, p7r and backup imports now report their result immediately.
- 20261022-01: Fix: in Artica, Generating a self-signed certificate from its settings now also records its validity dates and its PFX file.
- 20261022-01: Fix: in Artica Proxy, The listening-port certificate wizard now names the authority after the unit entered in the form and applies the new port settings without a full proxy restart.
- 20261022-01: Fix: in Artica, The default web-filtering certificate is no longer regenerated each time the setup wizard runs.
- 20261022-01: Add: in Artica, The AI assistant can now tell which internal machines a FortiGate sees, how much they download or upload, and when they were last seen.
- 20261022-01: Add: in Artica SIEM, A new Fortigate entry in the SIEM menu, shown only when FortiGate data is recorded, gathers the FortiGate status view and a FortiGate clients page with the top clients by data received and sent and a searchable client list filtered by tenant and FortiGate.
- 20261022-01: Add: in Artica SIEM, Each FortiGate client now records the tenant and the FortiGate that saw it, so identical internal addresses at two sites are no longer merged.
- 20261022-01: Add: in Artica SIEM, FortiGate traffic now builds an inventory of internal clients (MAC address, host name, operating system, address, bytes received and sent, last seen) with their traffic per destination in 10-minute slices; clients silent for more than three weeks are removed with their history.
- 20261022-01: Add: in Artica, The agent groups page can now show each group as a tile with its first agents, their state and version, and highlights groups with offline agents or alerts; a switch in the header returns to the table view.
- 20261022-01: Fix: in Artica, The help text about issuing one certificate for several hosts in the Let's Encrypt DNS request form is now translated.
- 20261022-01: Fix: in Artica, When the server cannot reach Let's Encrypt, certificate creation and renewal now stop immediately with a clear message saying that outbound traffic to Let's Encrypt is not open.
- 20261022-01: Fix: in Artica Proxy, The proxy auto-configuration (PAC) service now relays Let's Encrypt validation requests when it listens on port 80, so certificates can be issued and renewed on the same server.
- 20261022-01: Fix: in Artica, Let's Encrypt certificates are again issued and renewed on servers without the reverse-proxy web service: the validation is now answered directly on port 80 instead of waiting for a web server that is not running.
- 20261022-01: Add: in Artica, Monit 6 is now built automatically for Debian 12 and 13 from each new official release, with SSL, PAM and IPv6 support, ready to replace the older Debian package.
- 20261018-12: Add: in Artica, The settings of an existing firewall rule are now shown as a summary grouped by theme, and each setting is changed on its own in a small dialog.
- 20261018-12: Add: in Artica, The proxy and firewall objects page has been redesigned: filters by object type with counts, description of each object, on/off switches and the rules that use each object.
- 20261018-12: Add: in Artica, The firewall services page shows how many rules use each service, filters by protocol and status, and enables or disables a service with a switch.
- 20261018-12: Add: in Artica, The firewall rules page has been redesigned with a filter bar (search, interface, status), on/off switches, colour-coded directions and a count of the rules shown.
- 20261018-12: Fix: in Artica, The firewall rules list can be filtered by interface again, and moving a rule up or down now shows the new order immediately.
- 20261018-12: Fix: in Artica, The firewall rules page no longer fails to load when the firewall counters cannot be read.
- 20261018-12: Add: in Artica, The firewall services page uses the new table design, with a search box, the ports of each service shown as tags and its own address.
- 20261018-12: Fix: in Artica, The Suricata IDS service now reads and writes its settings through the Artica REST service instead of opening the cache database directly, so setting changes made in the Web Console are taken into account immediately.
- 20261018-12: Add: in Artica, The Suricata IDS package is now rebuilt automatically for Debian 12 and 13 whenever a new Suricata 8 release or a new Debian kernel is published, so its PF_RING driver always matches the latest kernel.
- 20261018-12: Fix: in Artica Proxy, The silent authentication page now shows accented chart labels and a capitalised time column.
- 20261018-12: Add: in Artica, The Artica Meta status dashboard has been redesigned: fleet health index, ring charts for the repository, agent and Debian versions and pending updates, and a live overview of the agents that need attention first.
- 20261018-12: Fix: in Artica Proxy, Silent authentication now presents users of the declared Active Directory domains without the domain prefix, so the user lists of the proxy rules match them as with NTLM and Kerberos.
- 20261018-12: Fix: in Artica Proxy, The silent authentication challenge now announces a valid NetBIOS computer name, as the NTLM specification requires.
- 20261018-12: Fix: in Artica Proxy, The authentication challenge now always returns a lightweight page, so browsers no longer drop the Windows sign-in handshake and show a login popup when user or Active Directory group rules are used.
- 20261018-12: Fix: in Artica, The GlusterFS storage pool now shows the real name of this node instead of "localhost".
- 20261018-12: Fix: in Artica, The last step of the GlusterFS volume creation wizard shows a clear summary and the full equivalent command, which was cut off on the right.
- 20261018-12: Fix: in Artica, When adding bricks to a GlusterFS volume, the proposed path is now on a dedicated disk not yet used by the volume instead of the system disk, and the help text explains that Use adds the disk to the list.
- 20261018-12: Fix: in Artica, The GlusterFS Status and Usage tabs no longer count the space of a volume deleted during the last hour.
- 20261018-12: Fix: in Artica, Disabling GlusterFS now asks for a clear confirmation listing what will be stopped, instead of a generic deletion message with an untranslated text.
- 20261018-12: Fix: in Artica, On an appliance with a single processor under load, the status of the services (uptime, running state) is no longer frozen on an old value.
- 20261018-12: Fix: in Artica, Active Directory LDAP connections now always use the recorded IP address of the domain controller instead of switching at random between its host name and its IP address.
- 20261018-12: Fix: in Artica Proxy, The Silent authentication page now shows the Active Directory groups of each recently identified user instead of an always empty column.
- 20261018-12: Fix: in Artica, Installing GlusterFS no longer needs access to a Debian package mirror: the GlusterFS package now carries the libraries it requires.
- 20261018-12: Fix: in Artica Proxy, HaCluster nodes no longer keep a replica of the IT charter database: they check and record the acceptances, and read the charters, directly on the load balancer, which ends the endless replication failures when the load balancer runs a newer database version.
- 20261018-12: Fix: in Artica Proxy, The web filtering service no longer opens a new connection to the IT charter database for every check: one connection is kept and reused, with bounded timeouts.
- 20261018-12: Fix: in Artica, A HaCluster failover master that starts while the backup node holds the floating IP address no longer records itself as the owner of that address.
- 20261018-12: Add: in Artica, The AI assistant can read the clock skew of the HaCluster nodes and, after approval, resynchronize a node on the load balancer.
- 20261018-12: Fix: in Artica Proxy, The HaCluster Windows console keeps showing the IT charter acceptances when the local socket of the charter database has disappeared, by reading the database on the loopback address instead.
- 20261018-12: Add: in Artica Proxy, The load balancer measures the clock of every cluster node and shows a yellow "Clock out of sync" label when it differs by 30 seconds or more, with a dialog to resynchronize the node from the web console or the Windows console.
- 20261018-12: Fix: in Artica Proxy, Cluster nodes without the chrony package now install it, so that they keep their clock synchronized on the load balancer instead of drifting until Kerberos fails.
- 20261018-12: Add: in Artica Proxy, Silent authentication identifies Windows users through NTLM without joining the domain and applies Active Directory group rules from the LDAP connection.
- 20261018-12: Fix: in Artica Proxy, A global blacklist holding both a domain and one of its subdomains no longer makes the proxy refuse every new configuration.
- 20261018-12: Fix: in Artica, Opening the GlusterFS Encryption tab after the Usage tab no longer leaves the Usage period selector, unstyled, in the page header: the Encryption tab now shows its own title, explanation and refresh button.
- 20261018-12: Fix: in Artica Proxy, After the Kerberos keytab is replaced, cluster nodes reload their authentication helpers, which kept the old key in memory and made browsers show a login popup.
- 20261018-12: Fix: in Artica, The GlusterFS mount wizard names its options in plain words (read-only, POSIX access control lists, do not record file access times) instead of showing the raw mount flags.
- 20261018-12: Fix: in Artica Proxy, The HaCluster status page now shows the address the load balancer really listens on: with failover it is the floating IP, flagged as such, instead of the configured interface that made clients aim at an address answering with a connection reset.
- 20261018-12: Add: in Artica Proxy, The HaCluster status page has a new design: four summary tiles, period selector, period totals that pick the chart to display, curve or raw view, CSV export, and a node table with state, weight share and last health check duration.
- 20261018-12: Add: in Artica, The AI assistant can read where the HaCluster load balancer really listens, to explain a connection reset on the proxy port.
- 20261018-12: Add: in Artica, The GlusterFS mount wizard gets the same design as the volume creation wizard: step indicator, source chosen between two cards showing which node serves the volume, live check of the mount point, backup servers and options as toggles, and a clearer summary.
- 20261018-12: Add: in Artica, The AI assistant can check the Kerberos authentication of a HaCluster again at once, on the operator's request and after approval, to confirm an Active Directory fix without waiting up to 10 minutes.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console has a "Check now" button on its Kerberos alerts: the load balancer keytab and the nodes in alert are checked again at once, instead of up to 10 minutes after a fix.
- 20261018-12: Fix: in Artica Proxy, The HaCluster Windows console no longer gives up after 4 seconds when the load balancer takes longer to apply the distribution rules.
- 20261018-12: Add: in Artica, The bricks step of the GlusterFS volume creation wizard shows which host is this appliance and which are the pool peers, tags every line as local, peer or outside the pool, checks each brick path as you type, and gains a step indicator.
- 20261018-12: Fix: in Artica, When the Artica daemon answers that an item does not exist (for example a GlusterFS volume deleted meanwhile), the console now shows that reason instead of a misleading "404 Not found, did you use the correct version of the Web API service?" error.
- 20261018-12: Add: in Artica, Bricks are added to a GlusterFS volume through a list: pick a node of the pool and a directory, review the bricks grouped by replica set, delete any line, then send them in one go.
- 20261018-12: Add: in Artica, The GlusterFS Usage tab now shows its period selector and its explanation in the page header, leaving the whole tab to the gauges and charts.
- 20261018-12: Add: in Artica, The GlusterFS Encryption tab is now a dashboard: setup progress, management encryption, pool nodes, volumes and external clients in tiles that open their own dialogs, and the certificate authority and node certificate in a settings card.
- 20261018-12: Add: in Artica, The GlusterFS client networks allowed through the firewall are now managed in a table: add one address or network at a time and delete any row, instead of editing a free-text list.
- 20261018-12: Add: in Artica, The GlusterFS Status tab is now a dashboard: service, version, pool nodes, volumes, storage used and self-heal in separate tiles, plus a firewall tile showing the open ports and the nodes and networks allowed to reach them.
- 20261018-12: Fix: in Artica Proxy, The HaCluster menu now shows "Windows console" instead of an untranslated label.
- 20261018-12: Fix: in Artica Proxy, The HaCluster Windows console certificate page now says that a certificate can also take a node out of Active Directory emergency mode and read the IT charter acceptances.
- 20261018-12: Fix: in Artica Proxy, The "Source IP address" label is no longer misspelled.
- 20261018-12: Fix: in Artica Proxy, The HaCluster Windows console names the web console page that issues its certificates as it appears in the menu.
- 20261018-12: Fix: in Artica Proxy, A cluster load balancer no longer ends up running two load-balancing engines after a reboot, and an existing duplicate is stopped automatically.
- 20261018-12: Fix: in Artica Proxy, With load balancer failover, the proxies now use the floating address of the active load balancer for DNS, time and reports, instead of an address that disappears after a failover.
- 20261018-12: Fix: in Artica Proxy, IT charter acceptances and charters now survive a load balancer failover and its return, and enabling the IT charter now also reaches the backup load balancer.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console shows an "ITCharter" menu while the cluster IT charter is enabled, listing which user accepted which charter and when, with a filter, in every language of the console.
- 20261018-12: Add: in Artica, The AI assistant can now summarize the firewall configuration export and import a firewall configuration exported by another appliance into a draft, always with an administrator approval and without applying anything until the draft is applied.
- 20261018-12: Add: in Artica, The firewall configuration can now be exported to a file and imported on another appliance: interfaces are matched by hand, object groups are recreated, and the imported configuration opens as a draft to preview before it is applied with confirmation.
- 20261018-12: Fix: in Artica Proxy, IT charters created on a cluster load balancer are now copied to the proxies and shown to users; before, the proxies never displayed them.
- 20261018-12: Fix: in Artica SMTP, Volume alerts now count an IPv6 client as its /84 network block, like the Postfix per-client limits, so a sender rotating its IPv6 addresses can no longer escape the alert.
- 20261018-12: Fix: in Artica SMTP, Volume alerts refuse an ignored network covering every address (/0), which would have silenced all alerts while the page showed them active.
- 20261018-12: Fix: in Artica Proxy, Searching the WAF threats or CrowdSec decisions for a partial IPv6 address such as "fd00" or "2a01" no longer fails with an error, and network searches like "10.0.0.0/8" or "fd00::/64" are validated before being used.
- 20261018-12: Fix: in Artica Proxy, IPv6 clients recorded by the WAF are no longer rescanned and reported as errors every three minutes.
- 20261018-12: Fix: in Artica, AbuseIPDB reputation now flags IPv6 clients too, instead of keeping only the first IPv6 address of the blacklist.
- 20261018-12: Fix: in Artica Proxy, The one-time IPv6 statistics conversion now stays fast on PostgreSQL versions older than 14, checks free disk space before rewriting a table, and waits for PostgreSQL when it is not started yet at boot.
- 20261018-12: Fix: in Artica Proxy, The nginx firewall watchdog now restores only the missing IPv6 blocking rule instead of rebuilding the whole firewall every ten minutes.
- 20261018-12: Fix: in Artica Proxy, Marking a bot as trusted and filling bot host names no longer scans the whole bots table for each address.
- 20261018-12: Fix: in Artica Proxy, Disabling the IT charter on a cluster load balancer now really removes it from the proxies, which re-enabled it by themselves a few seconds later, and stops the charter database on the load balancer.
- 20261018-12: Fix: in Artica, When the HaCluster failover master comes back online, it now takes the floating IP address back automatically even if its network was not ready at boot, without having to restart the failover service by hand.
- 20261018-12: Fix: in Artica, A GlusterFS mount that is slow to answer under heavy load is no longer restarted unless it stays unresponsive on two checks in a row.
- 20261018-12: Fix: in Artica, A GlusterFS node added while another node was disconnected now gains access to the encrypted volumes within minutes instead of up to an hour.
- 20261018-12: Fix: in Artica, Secondary text inside the light-coloured status widgets (failover state, floating IP address, cluster synchronisation details) is now displayed in a dark colour instead of white and is readable again.
- 20261018-12: Fix: in Artica Proxy, Visitors connecting over IPv6 now appear in the web statistics (Top IP, number of clients, countries and providers) with the same counters and geolocation as IPv4 visitors.
- 20261018-12: Fix: in Artica Proxy, Web Application Firewall reports are now recorded for IPv6 clients, and an audit file whose header cannot be read is kept in quarantine instead of being deleted.
- 20261018-12: Fix: in Artica Proxy, The "Deny access" button now really blocks an IPv6 address, and an IPv6 entry no longer prevents the IPv4 entries of the inbound block list from being applied.
- 20261018-12: Fix: in Artica Proxy, Access lists (stream access, WebDAV, directories) now accept a single IPv6 address.
- 20261018-12: Fix: in Artica Proxy, Searching for a full or partial IPv6 address now works in the Threats and CrowdSec pages.
- 20261018-12: Fix: in Artica Proxy, Bots seen from IPv6 addresses are now listed with their own address instead of being merged under 0.0.0.0.
- 20261018-12: Fix: in Artica Proxy, IPv4 /18 and /28 networks added to the inbound block list are now applied instead of being silently ignored.
- 20261018-12: Fix: in Artica Proxy, The Top IP counters no longer count a 10-minute window twice after a failed database insert.
- 20261018-12: Fix: in Artica Proxy, Enabling the central error page on a cluster load balancer now publishes the page immediately instead of up to ten minutes later, and refuses HTTPS without a certificate.
- 20261018-12: Fix: in Artica Proxy, Cluster proxies whose agent is older than 1.1.32 now also redirect blocked users to the load balancer's central error page.
- 20261018-12: Fix: in Artica Proxy, In a load-balancing cluster using the central error page, the web error page service of each proxy can no longer be disabled by a configuration replication or from the console, and it re-enables itself when the load balancer needs it.
- 20261018-12: Fix: in Artica Proxy, The web error page service no longer answers an internal error (500) on proxies where its page templates had never been generated.
- 20261018-12: Fix: in Artica Proxy, Blocked users of a load-balancing cluster are now redirected to the load balancer's central error page instead of each proxy's own page.
- 20261018-12: Fix: in Artica Proxy, Uninstalling the web error page service no longer leaves it running without supervision.
- 20261018-12: Fix: in Artica, A GlusterFS mount that has lost its connection to the volume is now remounted automatically within five minutes instead of staying broken.
- 20261018-12: Add: in Artica, GlusterFS now warns before the TLS certificates of the pool expire, and snapshots keep and restore the pool encryption material.
- 20261018-12: Add: in Artica, GlusterFS traffic can now be encrypted with TLS: a pool certificate authority is created on one node and imported on the others, management and data encryption are switched on from the console, and certificates can be issued for external clients.
- 20261018-12: Add: in Artica, Firewall changes can now be prepared in a draft, previewed (configuration changes, kernel rules added or removed, rules iptables would refuse) and then applied with confirmation or discarded in one step.
- 20261018-12: Fix: in Artica, Uninstalling a service on a system without systemd now also removes its boot links, and the leftover start script of the deprecated Tailon log viewer is removed.
- 20261018-12: Fix: in Artica, Service Pack rollback backups no longer pile up on the disk: only the three most recent rollback points of the current version are kept, checked every 4 hours.
- 20261018-12: Fix: in Artica, The capacity of a GlusterFS volume whose bricks have different sizes is now the size of its smallest copy, so fill alerts fire before the smaller disk is full.
- 20261018-12: Fix: in Artica, A GlusterFS brick that was replaced or removed no longer appears as offline in the usage view for an hour.
- 20261018-12: Fix: in Artica, Installing GlusterFS on Debian 13 no longer fails with "missing libraries": the libaio and liburing libraries required by the storage bricks are now installed automatically.
- 20261018-12: Add: in Artica AI, The assistant checks the Kerberos keytab of the HaCluster load balancer first and gives the right steps to rebuild a keytab that does not match the account of the service name.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console shows the Kerberos state of the cluster keytab held by the load balancer, and explains how to rebuild it when it does not match the account of the service name.
- 20261018-12: Add: in Artica Proxy, The HaCluster load balancer now checks its own Kerberos keytab, the only one of the cluster, and shows a red alert on its Kerberos page and above the node list when browsers cannot use it.
- 20261018-12: Fix: in Artica Proxy, The Kerberos alert no longer suggests moving the service name between accounts: it explains that the keytab does not match the account owning the name and gives the commands to rebuild it on the load balancer.
- 20261018-12: Add: in Artica AI, The assistant can check the Kerberos service name of a proxy, read the Kerberos state of each HaCluster node and, with approval, take a node out of the Active Directory emergency mode.
- 20261018-12: Fix: in Artica Proxy, The load balancer shows the current state of a node right after its report, instead of a state up to 10 minutes old (for example a node that has just left the Active Directory emergency mode).
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console shows a red Kerberos alert on a node whose service name cannot get a usable ticket, with the steps to fix it.
- 20261018-12: Add: in Artica Proxy, The Active Directory status page shows a red tile when the Kerberos service name of the proxy cannot get a usable ticket (name held by another account, not registered, or keytab rejected), with the steps to fix it.
- 20261018-12: Add: in Artica Proxy, Each HaCluster node now checks its Kerberos service name and reports a failure to the load balancer, which shows it on the node in the web console.
- 20261018-12: Fix: in Artica Proxy, A Kerberos ticket error logged by the proxy now triggers an immediate check that tells the administrator why single sign-on fails.
- 20261018-12: Add: in Artica SMTP, A new SMTP protocol hardening page protects against SMTP smuggling, using the strongest protection the installed Postfix release supports and the official workaround on older releases.
- 20261018-12: Add: in Artica SMTP, The SMTP protocol hardening page controls command pipelining: unauthorized pipelining is rejected and the PIPELINING and CHUNKING extensions can be withdrawn from the EHLO reply.
- 20261018-12: Fix: in Artica, A RDS Proxy session pattern set to disconnect now really ends the session and shows the reason to the user, instead of only reporting it.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console can take a node out of Active Directory emergency mode, after a confirmation explaining that its proxy currently lets everyone through without authentication.
- 20261018-12: Fix: in Artica Proxy, A Kerberos helper that reads the keytab while it is being rewritten no longer switches the proxy into Active Directory emergency mode.
- 20261018-12: Fix: in Artica Proxy, The Active Directory emergency mode caused by an unreadable keytab is now lifted automatically once the keytab is valid again.
- 20261018-12: Fix: in Artica Proxy, In an HaCluster, the nodes no longer alternate every three minutes between two different Kerberos keytabs, which reloaded the proxy twenty times per hour.
- 20261018-12: Fix: in Artica Proxy, The Active Directory emergency state of the cluster master is no longer replicated to the other proxies.
- 20261018-12: Add: in Artica Proxy, A node in Active Directory emergency mode can now be returned to normal authentication from the HaCluster nodes page.
- 20261018-12: Add: in Artica SMTP, A new Per-client limits page caps how many connections, messages and recipients one client address may submit per minute, including hosts of the trusted networks.
- 20261018-12: Add: in Artica SMTP, A new Volume alerts page warns when one client address submits an unusual volume of mail and when a provider such as Microsoft 365 or Gmail starts rate-limiting the server.
- 20261018-12: Add: in Artica, Trusted networks can now be declared in IPv6 and are honoured by the IPv6 firewall rules.
- 20261018-12: Add: in Artica, Country-based firewall rules now also apply to IPv6 traffic when the GeoIP database provides IPv6 ranges.
- 20261018-12: Add: in Artica, The firewall packet tester now evaluates IPv6 packets.
- 20261018-12: Fix: in Artica, Adding an IPv6 trusted network in the console no longer stores an empty network address.
- 20261018-12: Add: in Artica, The Service Pack update now displays a percentage while checking file integrity, while installing files and while compressing the backup.
- 20261018-12: Fix: in Artica, A corrupted Service Pack is now rejected before any file is replaced, so the system is never left partially patched.
- 20261018-12: Add: in Artica Proxy, Web-filtering database downloads now resume where they stopped after a network cut, instead of starting over, which makes large categories such as Malwares update reliably on slow or unstable links.
- 20261018-12: Add: in Artica, The RDS Proxy pattern detection now reads window titles on Windows 10, Windows 11 and Windows Server 2016 and later.
- 20261018-12: Fix: in Artica Compilator, Stopping the build daemon during a kernel module rebuild no longer sends a false failure report, and the interrupted rebuild is retried as soon as the daemon restarts instead of a day later.
- 20261018-12: Add: in Artica, The firewall now filters IPv6 with the same rules and interface policies as IPv4; each rule can apply to IPv4, IPv6 or both, and IPv6 filtering is enabled on update once the administrator confirms it.
- 20261018-12: Fix: in Artica Proxy, The HaCluster source-IP distribution rules page now says that a rule name is already used instead of showing an internal error.
- 20261018-12: Fix: in Artica Proxy, The HaCluster source-IP distribution rules page can save a rule again when the list of nodes cannot be loaded and the node identifiers are typed by hand.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console has a new Distribution menu to write, order, enable and apply the source-IP distribution rules of the load balancer, with a confirmation listing the rules before HAProxy reloads.
- 20261018-12: Fix: in Artica Proxy, Applying the source-IP distribution rules from the HaCluster Windows console reports whether the load balancer accepted the new configuration, and refuses rules targeting nodes that do not exist.
- 20261018-12: Add: in Artica Proxy, The node dialog of the HaCluster Windows console is split into a Proxy tab (traffic and service) and a System tab (CPU load, load average and memory of the node).
- 20261018-12: Add: in Artica Proxy, The node dialog of the HaCluster Windows console shows live charts of traffic, requests, CPU load, load average, memory and proxy clients, updated at each refresh.
- 20261018-12: Add: in Artica, Published servers (destination NAT) can now be reached from the internal network with their public address (NAT reflection), enabled by default and adjustable per publication.
- 20261018-12: Add: in Artica, Firewall objects can now hold host names, resolved every 5 minutes so that a rule follows the addresses of a partner's site or service.
- 20261018-12: Add: in Artica, The firewall rules list now shows when each rule was last used, and flags rules unused for 30 days or hidden by a rule placed above them.
- 20261018-12: Add: in Artica, The firewall can automatically ban, for a configurable time, sources outside trusted networks whose packets to the appliance are rejected too often, with a list of banned addresses and an unban button.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console shows the proxy nodes as tiles; clicking a node opens a dialog with its traffic, cache, service times, resources and versions.
- 20261018-12: Add: in Artica Proxy, The HaCluster agent of each proxy node now sends to the load balancer, every minute, the proxy metrics already collected on the node, so the HaCluster Windows console can display them.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console program and window now carry the Artica web console icon.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console shows the nodes running in Active Directory emergency mode with the same red label as the web console.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console has a new Settings menu that shows, read only, a summary of the general parameters of the load balancer.
- 20261018-12: Fix: in Artica Proxy, Node operations performed from the HaCluster Windows console are recorded in the administrators journal under the same conditions as every other administration operation, and name the certificate holder.
- 20261018-12: Fix: in Artica Proxy, The events journal of the HaCluster Windows console no longer overlaps the event code with the node name.
- 20261018-12: Add: in Artica Proxy, The HaCluster Windows console is now available in every language of the Artica web console: French, English, German, Spanish, Italian, Polish, Portuguese and Brazilian Portuguese.
- 20261018-12: Fix: in Artica Proxy, Empty rotated web-filtering log files are now purged automatically, instead of piling up by the hundreds of thousands in the log directory.
- 20261018-12: Fix: in Artica, A disabled Dynamic DNS agent no longer leaves the system monitor trying to start it every minute and a half.
- 20261018-12: Fix: in Artica Proxy, A leftover IDS monitoring rule from an earlier version is now removed when the IDS is disabled, instead of failing to start the IDS every minute and a half.
- 20261018-12: Fix: in Artica Proxy, Re-enabling a load-balancing node that was disabled now puts it back into service even when source-based routing rules still use it.
- 20261018-12: Fix: in Artica Proxy, A load-balancing node put back into service without restarting the load balancer is no longer reported down by its health checks until the next reload.
- 20261018-12: Fix: in Artica, The firewall events page no longer shows a wrong date (such as the 6th instead of the 16th) for firewall log lines written after the 9th of the month.
- 20261018-12: Fix: in Artica, Reloading or sharing the address of the firewall interface connectors page now opens that page instead of the network interfaces page.
- 20261018-12: Add: in Artica Proxy, A new "HaCluster Windows console" page issues certificates that let a Windows workstation supervise the load-balancing cluster in real time and drain, disable, take out of service or re-enable its nodes, and nothing else.
- 20261018-12: Add: in Artica, The firewall can reject and log traffic routed between interfaces when no connector allows it; published NAT services, replies and WireGuard tunnels stay allowed.
- 20261018-12: Add: in Artica, Firewall rules can carry a description and be grouped into collapsible sections.
- 20261015-17: Fix: in Artica, The HaCluster agent settings page no longer resets the emergency load threshold to 3 when "test every URL" is enabled, which made busy proxies leave the load-balancer every few minutes.
- 20261015-17: Add: in Artica, A GlusterFS brick can now be replaced from the volume details, for example after a disk failure: the new brick is picked among the server's disks, the volume keeps serving and the self-heal refills it from the other copies.
- 20261015-17: Fix: in Artica, The HaCluster load-balancer no longer crashes in a loop with HAProxy 3.4.5 and later: the TLS session cache workaround now applies to every affected HAProxy version, not only 3.4.4.
- 20261015-17: Fix: in Artica, Attaching or renewing the RDS Proxy certificate from the Certificate Center no longer disconnects the open RDP sessions.
- 20261015-17: Fix: in Artica, Removing the certificate chosen for the RDS Proxy now switches the gateway back to its self-signed certificate instead of keeping the previous one.
- 20261015-17: Fix: in Artica, The self-signed certificate of the RDS Proxy can now be loaded by the gateway, and the private keys of its certificates are no longer readable by other local users.
- 20261015-17: Fix: in Artica, Starting the Synology Active Backup agent now removes any snapshot kernel module left over from a previous agent version and rebuilds the module index, so after a Linux kernel update a backup no longer loads an incompatible module and crashes the server.
- 20261015-17: Fix: in Artica, The RDS Proxy TLS settings, certificate and session options now apply to the next connection as soon as they are saved, instead of waiting for the next service restart.
- 20261015-17: Add: in Artica, Each network interface linked to the firewall now has an outgoing default policy: with Finally deny all, only the connections accepted by outgoing rules can leave, while replies to established connections keep working.
- 20261015-17: Add: in Artica, A packet rejected by a Drop firewall rule is now logged with the name of the rule, so the firewall events page shows which rule blocked it instead of Default.
- 20261015-17: Add: in Artica, The firewall events page has a new Top tab listing the most active rules and the most rejected sources and ports over the last hour, 24 hours or 7 days.
- 20261015-17: Fix: in Artica, The source networks and excluded destinations of a masquerade entry are now applied and can be edited from the masquerade page; until now all the traffic of the interface was masqueraded.
- 20261015-17: Fix: in Artica, The packet counters of a firewall rule that logs its traffic no longer count each packet twice.
- 20261015-17: Add: in Artica, The GlusterFS status page now graphs the space used, the files waiting for self-heal and the connected clients of each volume over a day, a week and a month, and Artica warns when a volume or brick passes 85 % and 95 %, when a brick goes offline and when a self-heal stops progressing.
- 20261015-17: Fix: in Artica Proxy, The Web-filtering database update now shows the megabytes downloaded for large categories such as Malwares, its progress bar no longer stays at 90% for most of the update, and a download that stops receiving data is abandoned after two minutes instead of blocking the update for up to five hours.
- 20261015-17: Add: in Artica, A GlusterFS disk wizard lists the blank disks of this server, formats the chosen one in XFS with a single partition, mounts it, creates its brick directory and opens the volume wizard with that brick.
- 20261015-17: Fix: in Artica, Appliances running a Gold license no longer send the post-installation welcome notification to Artica Tech, so they no longer send any license, statistics or contact data to Artica Tech.
- 20261015-17: Fix: in Artica, A new RDS Proxy target now defaults to the RDP protocol, and the default error messages shown to refused users are spelled correctly.
- 20261015-17: Fix: in Artica, Outgoing firewall rules are now applied; until now every new outgoing connection was accepted before reaching them, so an outgoing Drop or Log only rule was shown active but had no effect.
- 20261015-17: Fix: in Artica, The firewall events page now shows the packets rejected by the firewall and the events of Log only rules, right after an update, and ping events no longer display the ports of the previous event.
- 20261015-17: Fix: in Artica, The Anti-DDoS option of a network interface, the DNS amplification protection and the Mark packets firewall rules are applied again; private source networks are now only dropped on interfaces set to act as WAN.
- 20261015-17: Fix: in Artica, Source NAT entries and Route packets to a node NAT entries are applied again by the firewall.
- 20261015-17: Fix: in Artica, A masquerade entry used by firewall rules now only masquerades the traffic of these rules and respects their exceptions.
- 20261015-17: Fix: in Artica, Firewall rules using a service whose ports are defined by a variable are applied with the right ports, and a rule whose service has no port is no longer applied to all traffic.
- 20261015-17: Fix: in Artica, The options, published servers and time restriction tabs of a firewall rule open again, and the time restriction tab no longer accepts malformed input.
- 20261015-17: Fix: in Artica, The firewall menu no longer shows duplicate entries, its configuration entry is no longer labelled imapd.conf, and the NAT, objects and bandwidth pages no longer display PHP warnings.
- 20261015-17: Fix: in Artica, The firewall parameters page shows the date of the last configuration in a readable format, and the maximum size of the firewall events log is kept when saved.
- 20261015-17: Fix: in Artica, The RDS Proxy now applies the handshake timeout, inactivity disconnection, keep-alive, minimum client TLS version, client cipher suites, legacy TLS fallback, ignore-logon-password and disconnect-on-user-change settings of the web console; they were saved but never used.
- 20261015-17: Add: in Artica, The RDS Proxy settings now offer the interactive login screen option and the option to close refused connections without showing the error, and reject out-of-range timeout values instead of silently ignoring them.
- 20261015-17: Add: in Artica, The RDS Proxy events page has a new Access events tab listing refused connections and detected patterns with the reason, user, client address and policy, filterable by user and reason.
- 20261015-17: Fix: in Artica, The RDS Proxy patterns tab now warns that window-title detection only works on Windows 2008 and 2012 targets with the classic theme, not on Windows Server 2016 and later.
- 20261015-17: Fix: in Artica, Formatting a disk now refuses the system disk, a mounted disk and a disk in use by LVM or RAID before anything is erased, and preparing a GlusterFS disk only proceeds if the disk is still completely blank.
- 20261015-17: Add: in Artica, The GlusterFS volume wizard now lists the disks of this server: a mounted disk fills the brick path in one click, and a blank disk can be prepared for GlusterFS (formatted in XFS and mounted) from the wizard itself.
- 20261015-17: Fix: in Artica, A GlusterFS brick is no longer created on the system disk when the disk declared for it in /etc/fstab is not mounted: the request is refused with the mount point to fix.
- 20261015-17: Fix: in Artica, Formatting a new disk no longer reports a success when the file system could not be created, and a freshly partitioned disk is no longer formatted before the system has made its partition available.
- 20261015-17: Fix: in Artica, XFS disks can be mounted again on servers where the system optimization had disabled the XFS driver, as soon as GlusterFS is installed or an XFS disk is declared.
- 20261015-17: Add: in Artica, When the AI assistant proposes to open GlusterFS to a client network wider than /8, such as 0.0.0.0/0, the approval screen now warns that every address in it will reach GlusterFS.
- 20261015-17: Fix: in Artica, GlusterFS requests refused by GlusterFS itself (volume already existing, brick on the system partition, volume still started) now return a clear refusal instead of an internal error, and deleting a busy GlusterFS mount no longer removes it from the boot sequence.
- 20261015-17: Fix: in Artica Proxy, Installing the proxy no longer schedules a removed notification script to run every minute.
- 20261015-17: Add: in Artica, Each RDS Proxy policy can now allow or block the clipboard (each direction and files), drives (read and write), printers, smart cards, serial ports and sound.
- 20261014-02: Fix: in Artica Proxy, Clients connected to a port without authentication, a transparent port or a cluster port can no longer reach the services the appliance only exposes on its loopback address through the proxy.
- 20261014-02: Fix: in Artica, Saving a CognixSys rule can no longer crash the management service.
- 20261014-02: Fix: in Artica, Firewall services, bandwidth limits, published addresses and CognixSys rules are now checked before being saved and applied immediately, without an Apply or Compile button.
- 20261014-02: Fix: in Artica, A firewall service still used by a rule can no longer be deleted.
- 20261014-02: Fix: in Artica Proxy, Access rules that are not tied to a specific listening port apply again to every port, including ports without authentication, instead of being ignored since the update.
- 20261014-02: Fix: in Artica Proxy, Access rules restricted to the standard or transparent method, or placed in a rule folder bound to a port, are applied to the right port again instead of being ignored.
- 20261013-21: Add: in Artica, The RDP bastion can be connected to an Artica SIEM with its own certificate, renewed automatically, from the new RDS Proxy SIEM page, which can test the link before connecting.
- 20261013-21: Fix: in Artica, Messages held for a dangerous link are labelled as such in the mail quarantine, can be filtered, and show the dangerous domains in their details.
- 20261013-21: Fix: in Artica, The URL threat scan settings dialog shows the security categories heading at its place instead of above the first switch.
- 20261013-21: Fix: in Artica, NAT and masquerade rules are now checked before being saved and applied automatically, without an Apply button.
- 20261013-21: Fix: in Artica, A NAT rule or a masquerade still used by firewall rules can no longer be deleted, and changing the type of a NAT rule keeps its firewall rules attached.
- 20261013-21: Fix: in Artica, The destination of a local redirection NAT rule is displayed correctly in the firewall rules page.
- 20261013-21: Add: in Artica, The Postfix log explorer shows its search, status and instance filters in the page header.
- 20261013-21: Fix: in Artica, The Postfix log explorer no longer shows an untranslated label when the live feed is unavailable.
- 20261013-21: Add: in Artica, The URL threat scan status tab summarises the service health, its prerequisites, the cloud state and lost events, with a link to the log explorer.
- 20261013-21: Fix: in Artica, Firewall rules, their options, schedules, deep packet inspection protocols and services are now checked before being saved and are applied automatically, without an Apply button.
- 20261013-21: Fix: in Artica, Deleting a firewall rule no longer leaves its deep packet inspection entries behind.
- 20261013-21: Add: in Artica, Firewall rules can use the Log only and Return actions, and the rules page shows why a rule cannot be applied.
- 20261013-21: Add: in Artica, The URL threat scan statistics show their period and category filters in the page header, with summary cards and ranked tables.
- 20261013-21: Add: in Artica SIEM, The SIEM now receives and keeps for one year the access events of the RDP bastion (authentications, second-factor challenges, session openings and closings), searchable by user, address, target or session.
- 20261013-21: Add: in Artica, The URL threat scan parameters show today's activity, the cloud state and each setting as a readable card.
- 20261013-21: Fix: in Artica, Without a licence, the URL threat scan settings dialog shows a single switch that saves on click.
- 20261013-21: Fix: in Artica, Firewall rules with the Log or Return action, and rules attached to a masquerade, are now applied instead of being silently ignored.
- 20261013-21: Fix: in Artica, The firewall watchdog no longer rebuilds the whole firewall when a rule is refused by the kernel; the administrator is notified with the kernel error instead.
- 20261013-21: Add: in Artica, The firewall rules page shows whether changes are waiting, being applied or applied, and lists the rules refused by the kernel.
- 20261013-18: Fix: in Artica, RDS Proxy policies created with an older version of the console, whose session time was saved empty, are listed again instead of failing with a database error.
- 20261013-18: Add: in Artica, Every change to RDS Proxy members, targets, policies, their networks and time slots, the login page logo, session disconnections and recording deletions is now recorded in the administrators activity log.
- 20261013-18: Fix: in Artica, The periodic check of the local databases no longer releases the locks of the Artica service on them, which could let another program delete pending changes and make recently saved settings (such as RDS Proxy members) disappear.
- 20261013-18: Fix: in Artica, RDS Proxy members, targets and policies are now saved through the Artica service with full validation, so duplicate names and invalid networks or time slots are refused with a clear message instead of being silently ignored.
- 20261013-18: Fix: in Artica, Deleting an RDS Proxy policy, member or target now removes all of its links in a single operation.
- 20261013-18: Fix: in Artica, Several firewall pages of the web console no longer allow database or system command injection through crafted requests, and they now verify the firewall administrator privilege on the server side.
- 20261013-18: Fix: in Artica, Firewall rules that send traffic to another gateway (next hop) or to a transparent proxy use the configured port again instead of always falling back to 8080.
- 20261013-18: Fix: in Artica, Firewall rules defined for all interfaces are no longer copied into every NAT rule, and redirect NAT rules are accepted by the kernel firewall again.
- 20261013-18: Fix: in Artica, The trusted network is now accepted on the default firewall chain, and rules defined for all interfaces are no longer inserted twice.
- 20261013-18: Fix: in Artica, The firewall watchdog no longer rebuilds the whole firewall in a loop because of rules whose action cannot be applied (link balancing, log, return, masquerade rules); the administrator is notified instead, and simultaneous rebuilds are now serialized.
- 20261013-18: Fix: in Artica, Bandwidth limits changed in the traffic shaping page are applied and removed immediately again, including when an entry is deleted.
- 20261013-18: Fix: in Artica, Disabling an RDS Proxy policy now actually prevents the connections it allowed.
- 20261013-18: Add: in Artica, Each refused RDS Proxy connection now records the precise reason, such as a network or time slot not allowed by the policy.
- 20261013-18: Fix: in Artica, RDS Proxy targets now use NLA with NTLM by default, so connections to Windows servers no longer end with "CREDSSP Kerberos authentication failed, NTLM not allowed"; each target offers a Network Level Authentication choice: NTLM, Kerberos then NTLM, Kerberos only, or no NLA.
- 20261013-18: Add: in Artica, Links in incoming mail are now checked against the Artica cloud categories, short links are followed to their final site and random-looking domains are flagged; a message with a phishing, malware or spyware link is tagged or held in quarantine, and the domains and categories found appear in a new statistics page and in the daily report (Corporate license).
- 20261013-13: Fix: in Artica, Task progress bars now show the action being performed (restarting, installing, reconfiguring a service…) instead of a generic "Running" title.
- 20261013-13: Fix: in Artica Proxy, A cluster master no longer publishes a proxy configuration that the proxy itself refuses; the nodes keep the last valid package until the configuration is repaired.
- 20261013-13: Fix: in Artica Proxy, A cluster node now checks a received proxy configuration before keeping it and restores its previous configuration if the proxy refuses it, instead of losing its workers one by one and being unable to restart hours later.
- 20261013-13: Fix: in Artica Proxy, A proxy reload is no longer reported as successful when the automatic repair left a configuration the proxy still refuses, and a repaired configuration is now actually loaded.
- 20261013-13: Fix: in Artica, Phishing sites hosted on website builders such as weebly.com or godaddysites.com are now filed under Phishing, including when the platform carries several categories.
- 20261013-13: Fix: in Artica, Phishing sites hosted on shared platforms such as vercel.app, github.io or blogspot.com are now filed under Phishing instead of being skipped because the platform itself is already categorized.
- 20261013-13: Fix: in Artica, On the DNS servers page, the progress bar of a service restart is no longer erased by the automatic status refresh before the task ends.
- 20261013-13: Fix: in Artica, The quarantine report now tells users to click Release or Receive when it lists newsletters and notifications, matching the button shown on those messages.
- 20261013-13: Fix: in Artica, The mail quarantine list labels the source of held messages Anti-spam instead of Spam, so a held newsletter is no longer shown as spam.
- 20261013-13: Add: in Artica, Task progress bars now show a card with the task name, the current step, a large percentage and a clear success or failure state.
- 20261013-13: Fix: in Artica, The audit service no longer switches the whole appliance to single-user mode when the disk is nearly full: it now suspends audit logging and the appliance keeps running, and an audit service found stopped is started again automatically.
- 20261013-13: Fix: in Artica, A Service Pack refused during installation because one of its files is missing or corrupted now restores the files it had already replaced and removes its temporary copies, and the files left by an interrupted installation are cleaned up automatically.
- 20261013-13: Fix: in Artica, Old audit logs are now purged automatically, keeping only the two most recent archives, instead of accumulating in /var/log/audit until the disk is full.
- 20261013-13: Fix: in Artica, The RDS Proxy now reads its generated configuration, so users are no longer refused with "authentication service unavailable" at the login screen.
- 20261012-17: Add: in Artica, The Web console skin settings have a Reset button that, after confirmation, removes every design customization and restores the factory look.
- 20261012-17: Add: in Artica, The OpenLDAP API can now rename a group, list its members, change an account's primary group and delete a group while deleting or moving its accounts, never leaving an account without a primary group.
- 20261012-17: Fix: in Artica, The mail log tracker now recognises the classification lines written for messages screened by the Rspamd filter, so newsletter and notification counts and learned-correspondent bypasses are recorded instead of being mistaken for delivery attempts.
- 20261012-17: Add: in Artica Proxy, A web categories console certificate can now be issued without compilation rights: its holder feeds the categories and the scheduled task compiles them.
- 20261012-17: Add: in Artica Proxy, The Timeouts tab of the general settings now shows each value as a tile and opens the settings in a dialog when a tile is clicked.
- 20261012-17: Fix: in Artica, Durations of exactly one minute, hour or day are now translated instead of showing a raw placeholder.
- 20261012-17: Fix: in Artica, Clicking the edit icon on the right of a settings tile no longer opens the same dialog twice.
- 20261012-17: Add: in Artica, The mail quarantine can classify newsletters and automatic notifications as Infomail and deliver, tag or hold them per domain, with a dedicated section in the quarantine report.
- 20261012-17: Add: in Artica, The categories catalogue service can now tell when the next compilation of the web-filtering and DNS category databases is scheduled.
- 20261012-17: Add: in Artica, Every change made through the categories catalogue service (sites, categories, certificates, peers, licence, manual tasks) is now recorded in the administrators' activity log with the name carried by the client certificate.
- 20261012-17: Fix: in Artica, The statistics database (PostgreSQL) no longer stops for good one year after installation on hardened systems: its service account is no longer subject to password expiry, and an already expired account is repaired automatically.
- 20261012-17: Fix: in Artica, The daemon no longer freezes when the statistics database is down: connections through PgBouncer now give up after 5 seconds, so the automatic restart of PostgreSQL is no longer blocked.
- 20261012-17: Add: in Artica, The categories catalogue service now accepts the Windows categories console over its secure port, and an operator holding the AI privilege can manage the sites of the official categories from it.
- 20261012-17: Add: in Artica, The categories catalogue can issue a password-protected certificate bundle for the Windows categories console from the command line, the API or the Web console.
- 20261012-17: Add: in Artica Proxy, The global rules page shows each permanent authorization as a tile with its own switch, summary tiles, and category and text filters; a switch takes effect immediately.
¶ List of available Hot Fixes
Get the Hot Fixes here:
https://www.articatech.com/hotfixes.php?main=4.50.000000&sp=10
¶ Apply the HotFix
- On the left menu, click on “
Your System” > “Update” - Click on the button “Manual update” and upload the artica-4.50.000000.tgz downloaded file
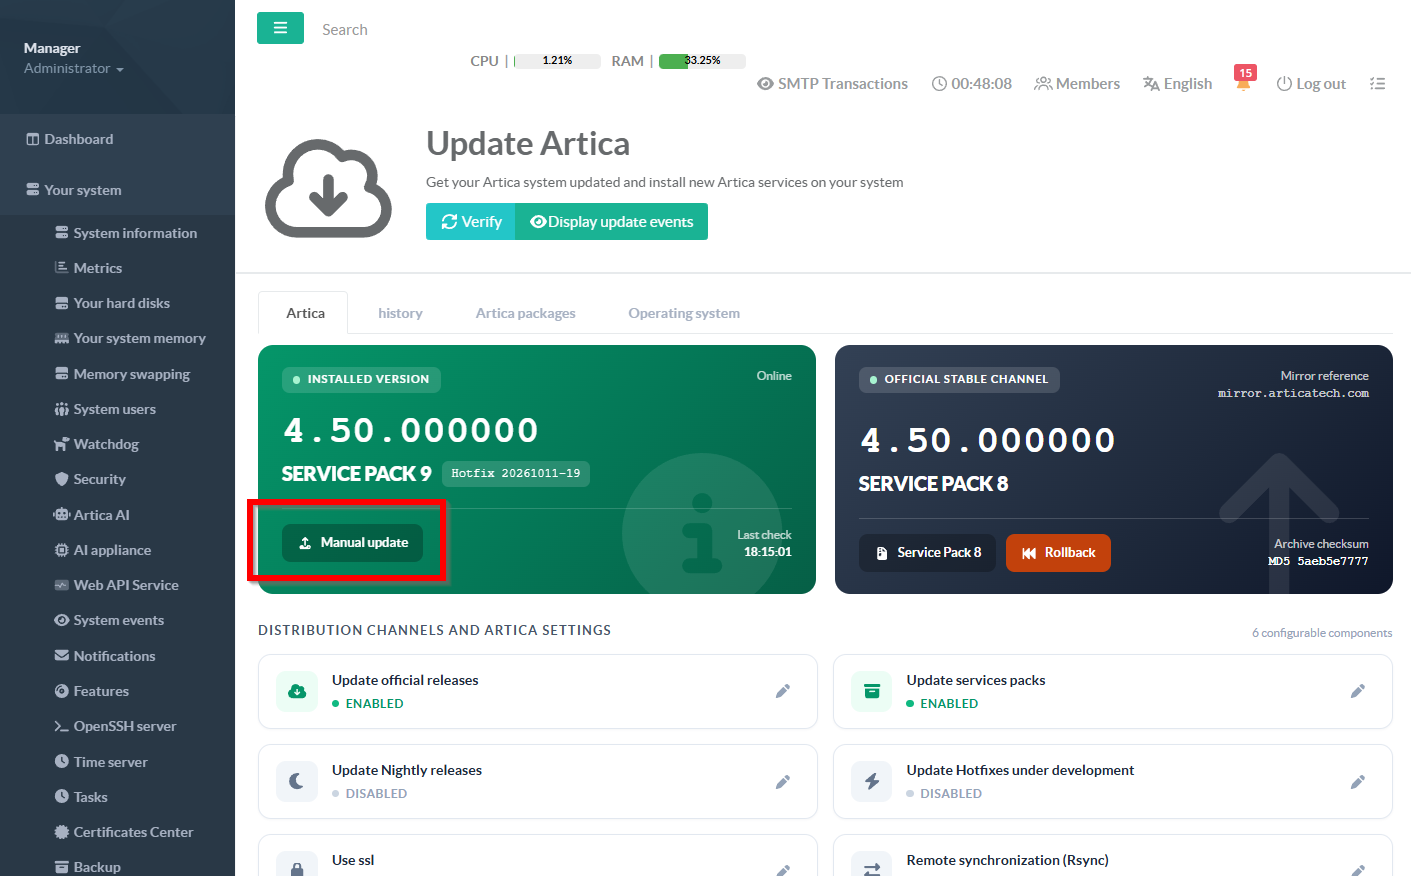
- Click on the Artica tab
- You will find a “Current Hotfix" row with the applied version.