← Back to the RDS Proxy main page
Instead of creating every user and server in the RDS Proxy, you can link Active Directory groups:
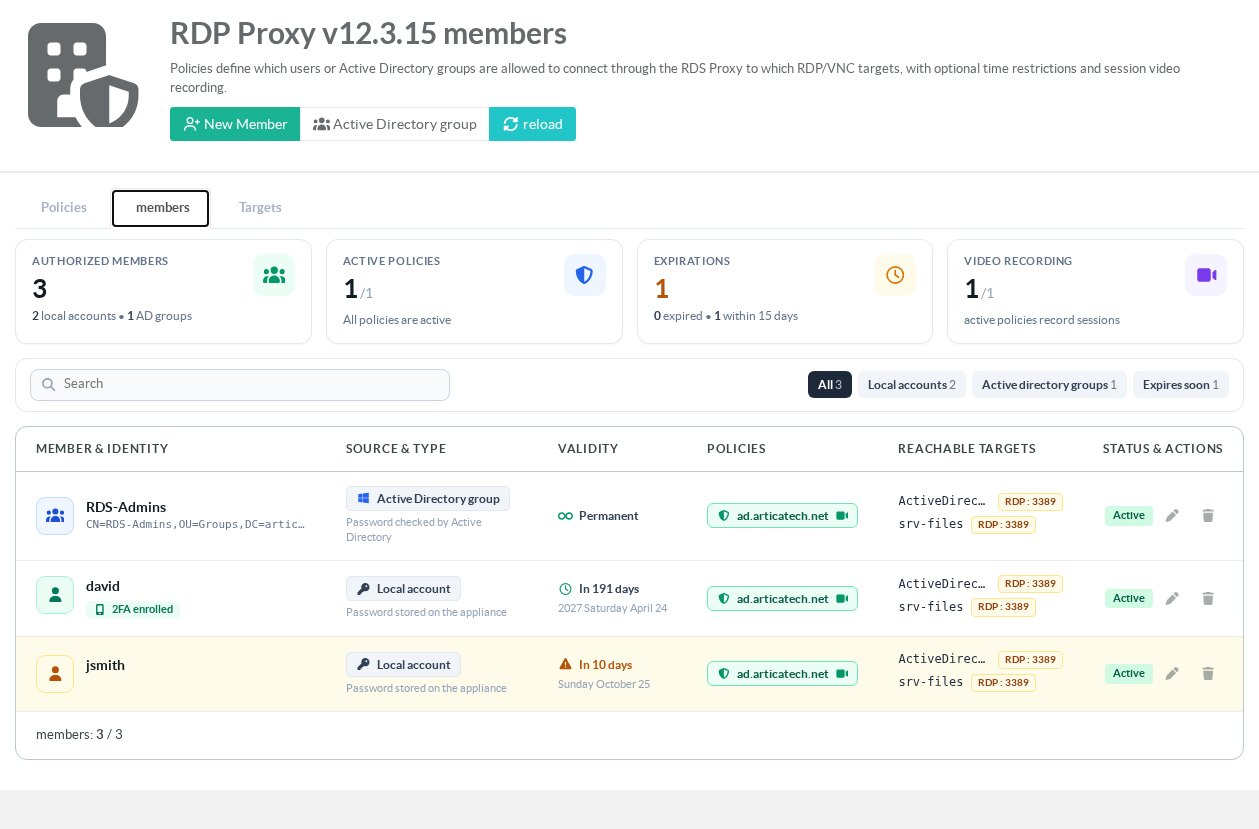
- an AD group of users, as a member: every user of the group may log in with their Active Directory account;
- an AD group of computers, as a target: every computer of the group is published.
The appliance needs the Active Directory feature and an Active Directory connection; see Set up your Active Directory connection. Users of an AD group are not masked: they log in with their own Active Directory credentials, and those credentials are also used on the target computers.
¶ Authorize an AD group of users
- Open RDS Proxy » Policies » Members.
- Click Active Directory group, search for the group and select it.
- Link the group to a policy (policy » Members tab).
¶ Publish an AD group of computers
- Open the Targets tab.
- Click Active Directory group and select the group of computers. The target lists the computers of the group.
- Link the target to a policy.
When a user connects, the target selector lists the computers of the group. The gateway resolves each computer name with the DNS servers of the appliance.

¶ Kerberos
To authenticate to the computers with Kerberos, choose Kerberos, then NTLM as the NLA mode of the target. See Network Level Authentication mode.