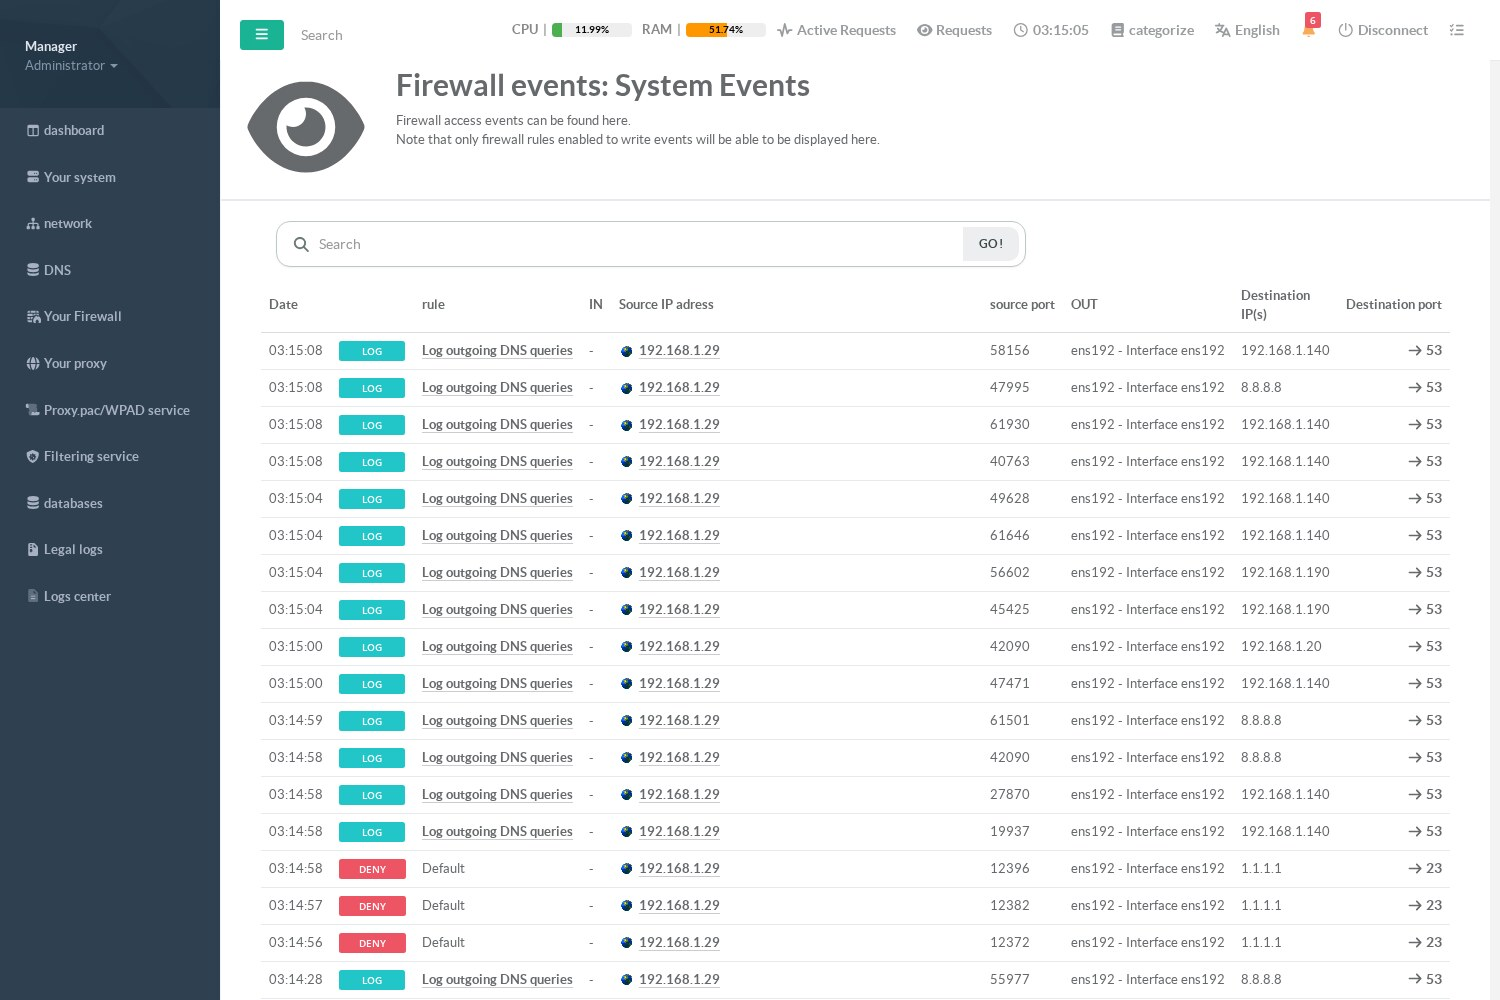
The firewall writes its events to the kernel log. Artica collects them into
/var/log/firewall.logand displays them in Your Firewall › Events.
¶ Which events are logged
Only some packets are written, to keep the log readable:
| Event | When | Shown as |
|---|---|---|
| Rejected packets | Always: every packet rejected by a Drop rule, by the Finally deny all policy or by the Anti-DDoS connection limits is logged (at most 1 line per second, bursts of 5). | DENY, rule Default |
| Log only rules | Every packet matching a rule whose action is Log only (at most 1 line per second per rule). | LOG, with the name of the rule |
| Rules with Log All Events | Every packet matching a rule whose Log All Events option is checked, before its action is applied. | The action of the rule, with its name |
| Log all events (global option) | Every packet accepted or rejected by a rule or a policy, on every interface. See Parameters. | PASS / DENY |
| Port scans | On an interface linked to the firewall, packets with impossible TCP flags (XMAS, NULL and FIN scans), at most 3 per minute. | Scanner |
A rejected packet is reported with the rule Default even when a Drop rule rejected it: all rejections go through the same reject target, which does not know the rule. To see which rule blocks a flow, use the Packets column of the rules table, or add the Log All Events option to the rule.
¶ Read the table
- IN / OUT: the interface the packet came from or left by. Traffic of the appliance itself has no IN interface.
- Source IP address: click it to see what Artica knows about this address.
- source port / Destination port: empty (
-) for protocols without ports, such as ICMP (ping). - The search field filters the lines (address, port, rule name…).
¶ Example: observe a flow before blocking it
- Create a rule with the action Log only, for example on the service dns, with Outgoing Rule checked to see the DNS queries the appliance sends.
- Open Events: each query appears with the LOG label and the name of the rule.
- When you know which servers are used, replace the rule by Accept and Drop rules.
¶ Storage and forwarding
- Events are kept in
/var/log/firewall.log. When the file exceeds the size set in Export log if size exceed (100 MB by default), it is emptied. - Backup Firewall events (Parameters): before being emptied, the file is copied to the log rotation directory, so no event is lost.
- Do not store events locally: events are only forwarded to the remote syslog servers and to the SIEM, and the Events page stays empty.
¶ From the command line
# Last events
tail -f /var/log/firewall.log

# Rejections only
grep "ARTICA:REJECT:" /var/log/firewall.log

# Events of the "Log only" rule number 3
grep "ARTICA:LOG:3:" /var/log/firewall.logLog prefixes: ARTICA:REJECT: for rejections, ARTICA:LOG:<rule id>: for Log only rules, FIREHOL:… for the other events (rules with Log All Events, policies, port scans).
¶ No events?
- Traffic from the trusted networks is accepted before the interface rules: it never reaches a Log only rule of an interface.
- Check that the rule is Active and that its Packets counter increases.
- Check that Do not store events locally is off.