← Back to the RDS Proxy main page
The RDS Proxy can require a time-based one-time code (TOTP), such as those generated by Microsoft Authenticator, Google Authenticator or FreeOTP, after the password. It is enabled per policy.
¶ Enable the second factor
- Open the policy in RDS Proxy » Policies.
- Turn on Require the second factor (TOTP) and apply.
The second factor requires RDP Proxy authenticator 1.3.0 or later; with an older version, the policy shows a warning and the code is not asked.
¶ What users see
- At the first connection after the policy requires it, the gateway displays a secret key in the Remote Desktop window. The user adds this key to their authenticator app, then types the code the app shows.
- At each following connection, the user types the current 6-digit code after their password.
Five wrong codes in a row lock the account for 15 minutes. Each challenge, success and failure is written to the access events and sent to the SIEM.
¶ Manage the users
Open RDS Proxy » Second factor. The page lists the users with their enrollment date, last use, failed attempts, lock and exemption.
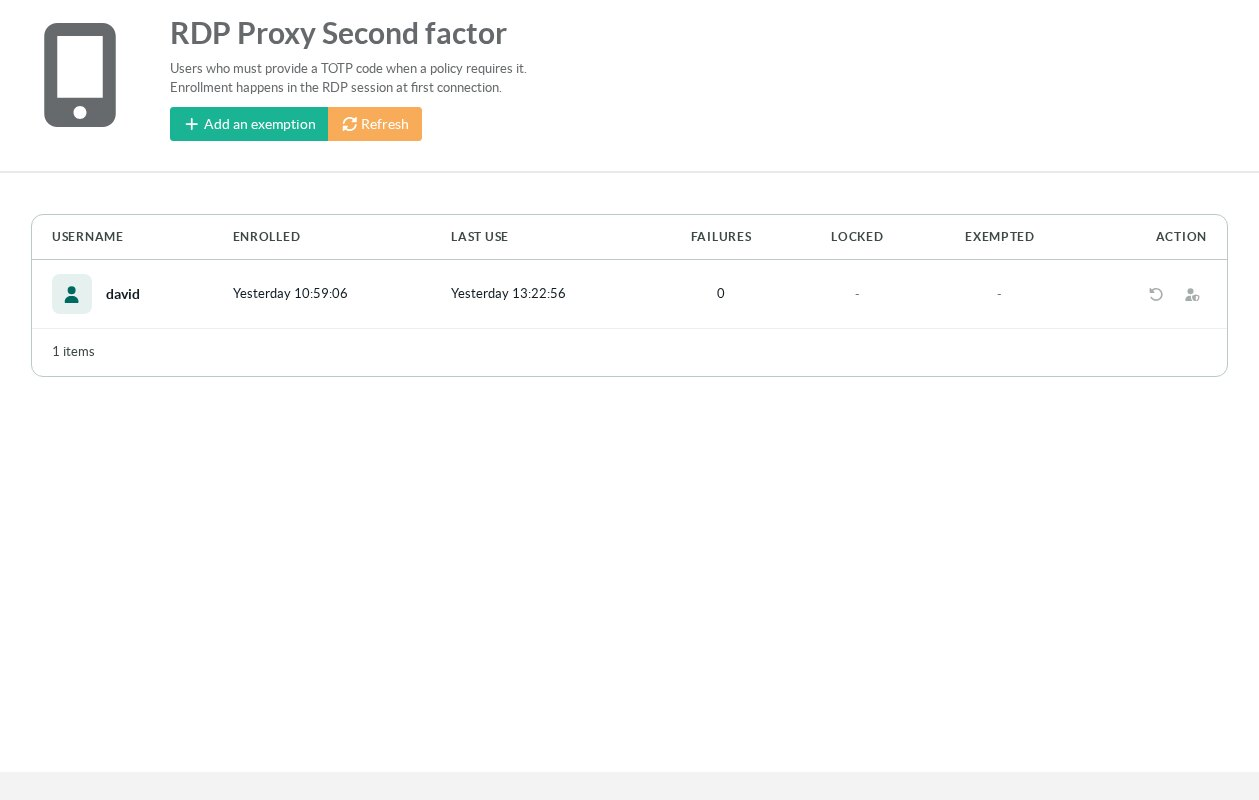
- Reset: deletes the user's secret. They enroll again at their next connection (lost or replaced phone).
- Unlock: clears a lock before the 15 minutes are over.
- Add an exemption: the user is never asked for a code, even when their policy requires it (service accounts, emergency access).
A user is identified by their account name, whatever its form: CORP\jdoe, jdoe@corp.local and jdoe are the same user.
The secrets are encrypted with a key stored on the appliance (
/etc/artica-postfix/rdpproxy-mfa.key). It is included in Artica backups; without it, every user must enroll again.