CVE-2021-26708
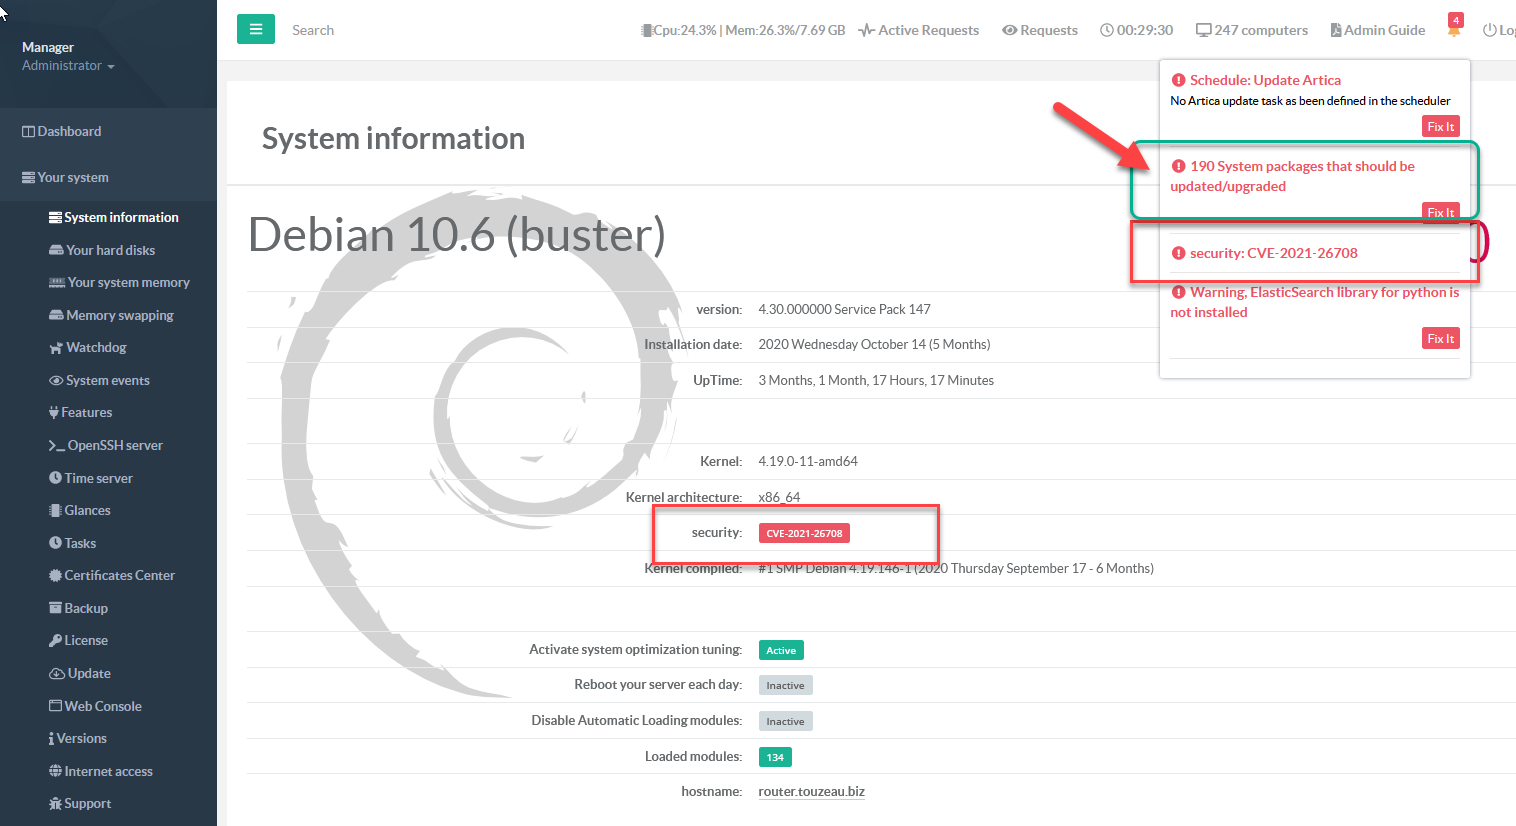
You should see CVE-2021-26708 inside the Artica Web console after updating to latest Artica version
The CVE-2021-26708 describes a local privilege escalation was discovered in the Linux kernel before 5.10.13.
Multiple race conditions in the AF_VSOCK implementation are caused by wrong locking in net/vmw_vsock/af_vsock.c.
The race conditions were implicitly introduced in the commits that added VSOCK multi-transport support.
The Web Artica console notify that your system must be updated in order to fix this security hole. ( Artica v4.30 SP 151 or above)
The red information can be displayed in top-right notification and in System information section.
Too fix it : Just upgrade the system by click on “Fix it” on the xxx packages that should be upgraded, Clik on upgrade the system and reboot the server