Domain Routing
The DNS firewall can forward requests to other DNS servers of your choice depending on the requested domain.
Return back to main Artica DNS Firewall section
The DNS firewall can forward requests to other DNS servers of your choice depending on the requested domain.
So it acts as a DNS router
To illustrate this feature, we will use our DNS firewall as a centralized DNS server.
It will be able to forward requests to unknown domains using public DNS but also to forward requests to our Internal Active Directory domain "articatech.nux" to the Active Directory DNS service
In the spirit of ACLs, a DNS firewall rule is constructed by adding up objects.
In our case, we will associate a "domains" object with a "destination DNS server" object
- This operation is built into the firewall rules available in the section DNS / DNS Firewall / Firewall rules
A) Create the Rule
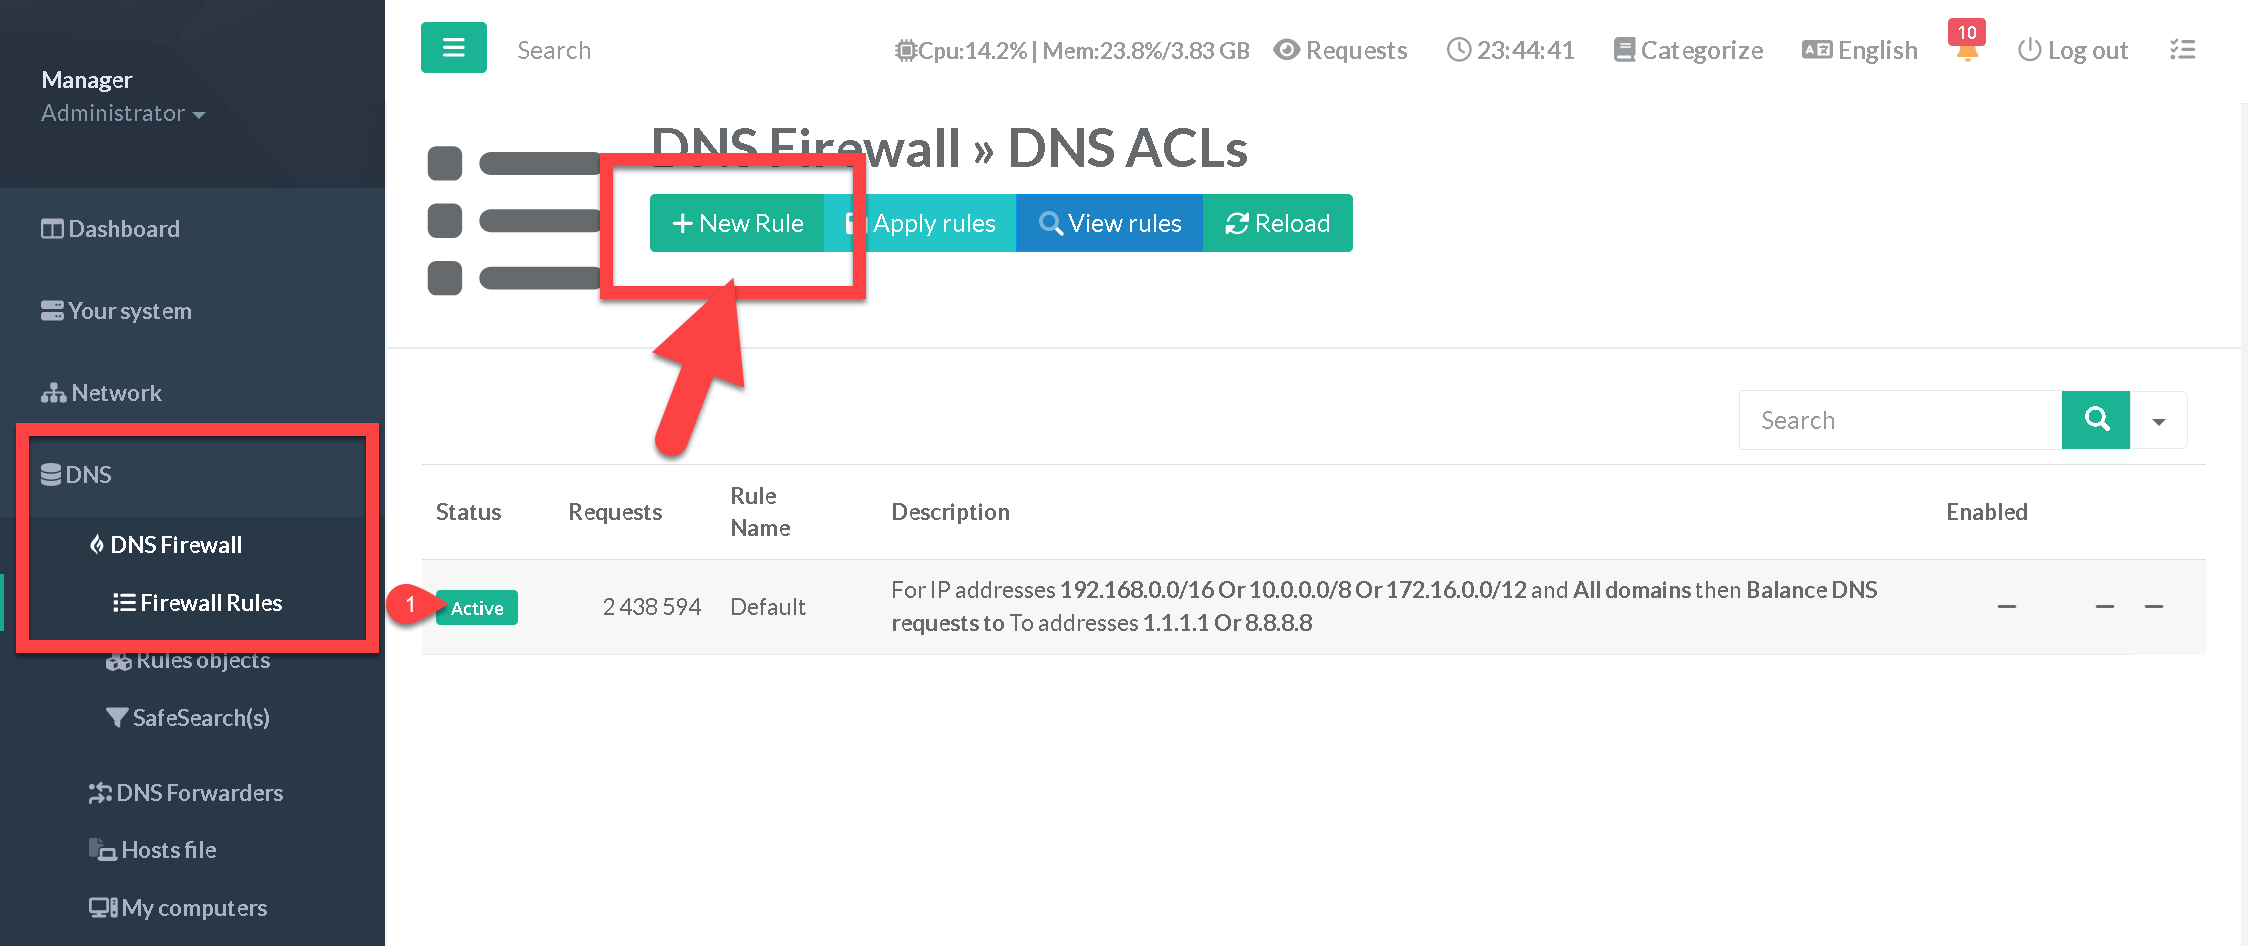
You can see that there is a default rule that already exists, it is designed to relay unknown domains to the public DNS servers that you have defined in the general DNS forwarders section
- Click on the “New rule” button
- In Action, choose “Balance DNS Requests to” and set a rule name
- Click on Add button
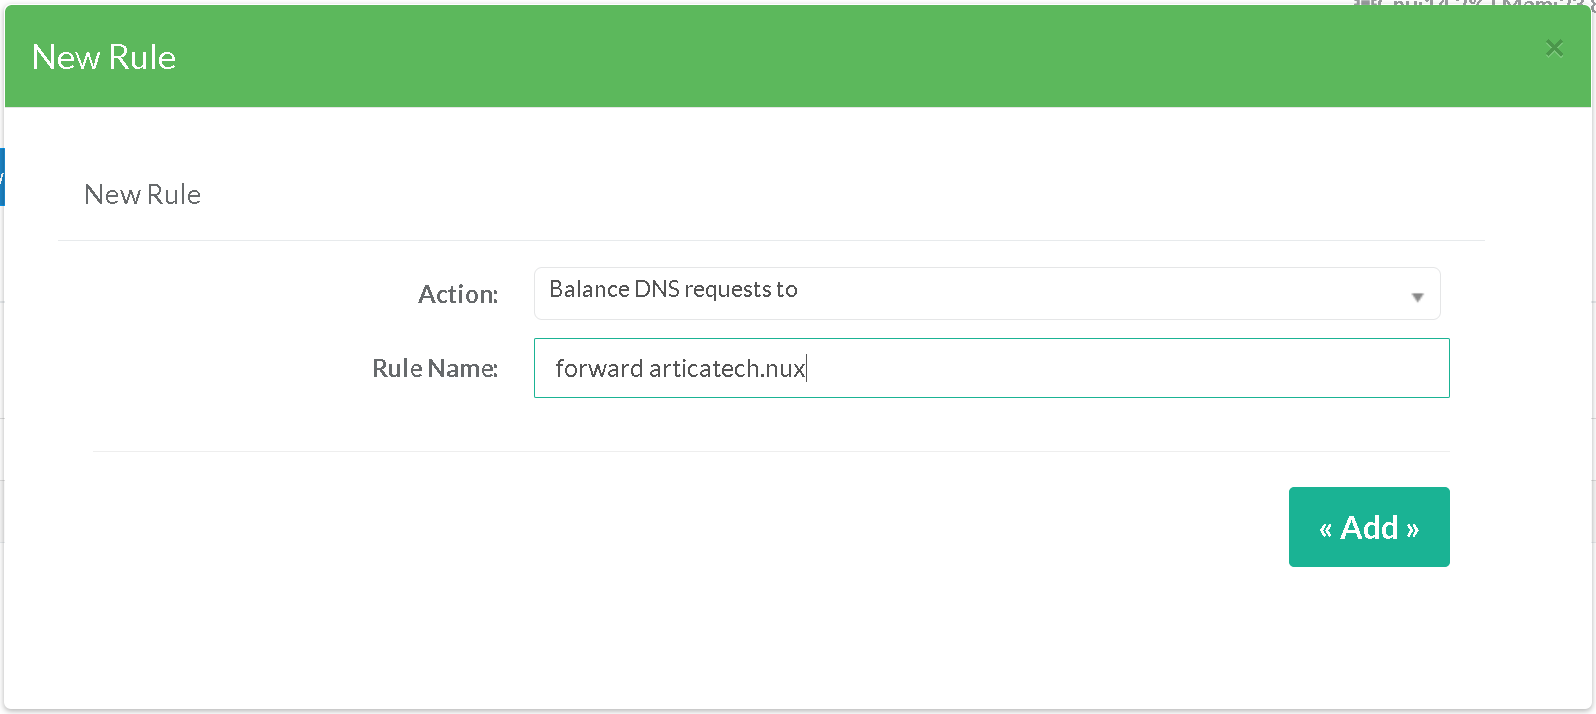
Although we have only one Active Directory server, the word "balance" is important because in addition to the routing functionality, the DNS firewall can also perform load balancing
- Once the rule is created, click on it to display its details.
B) Create the domain object
- Click on the “Objects" tab.
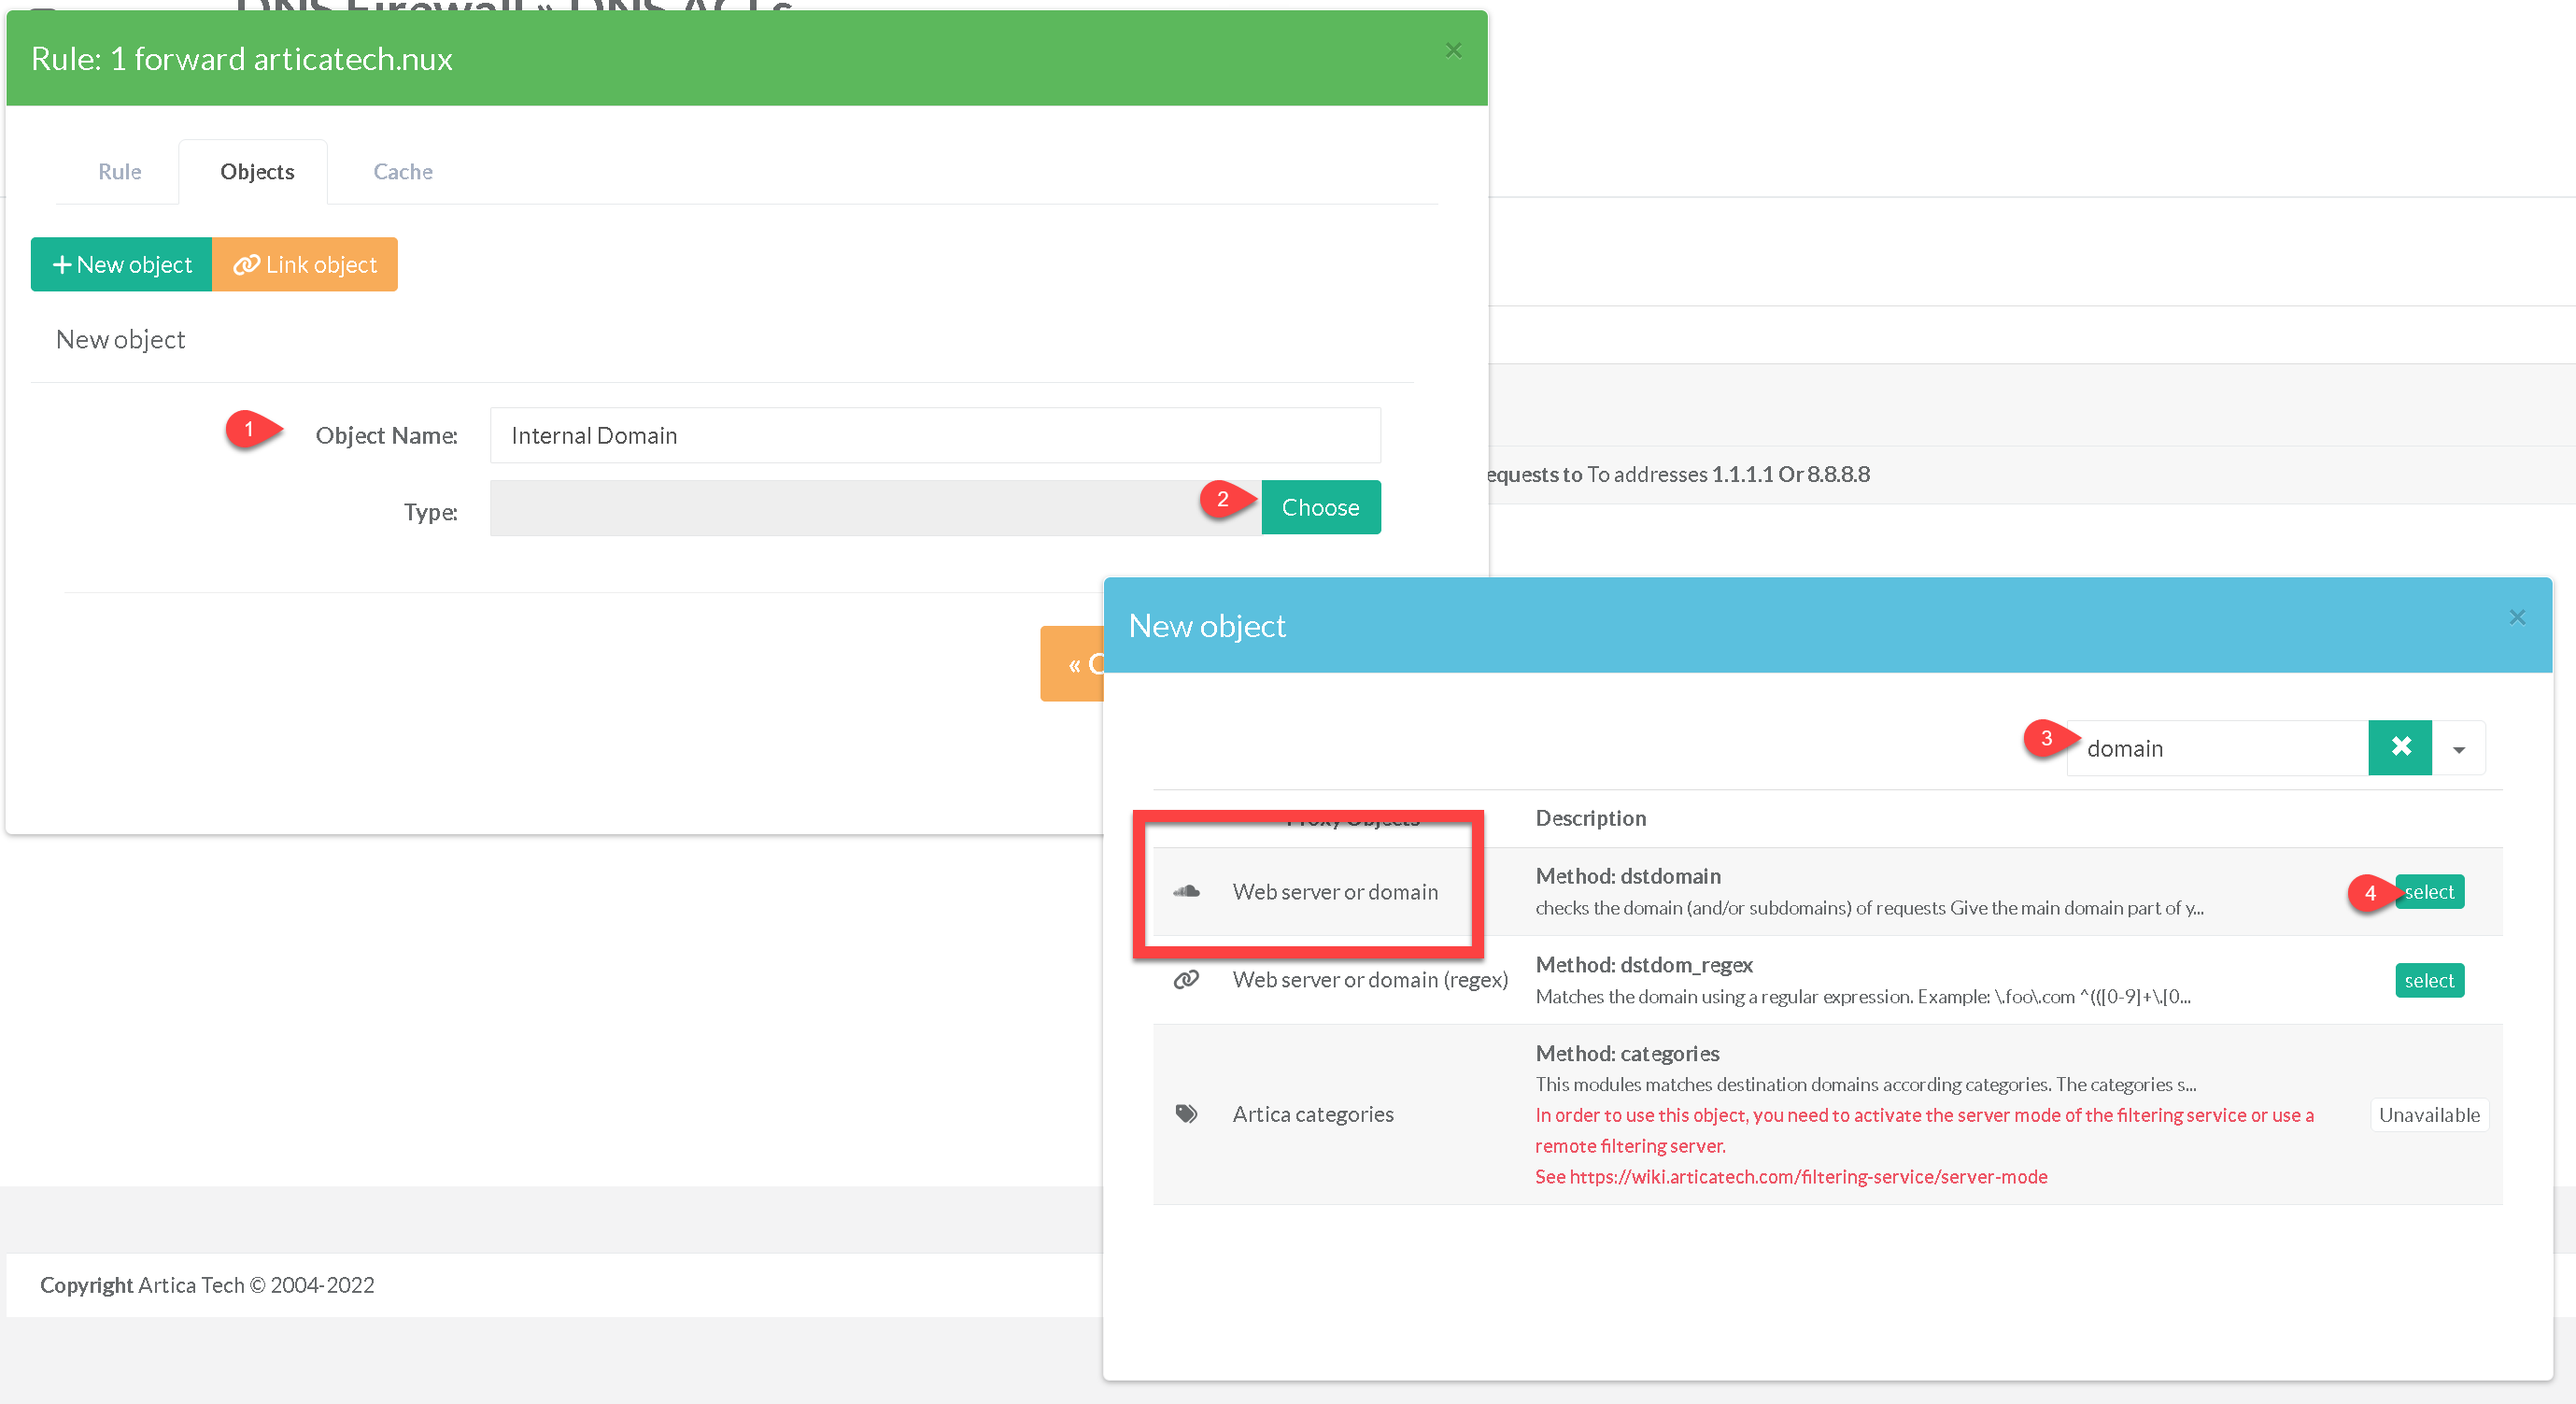
- Click on “New Object”
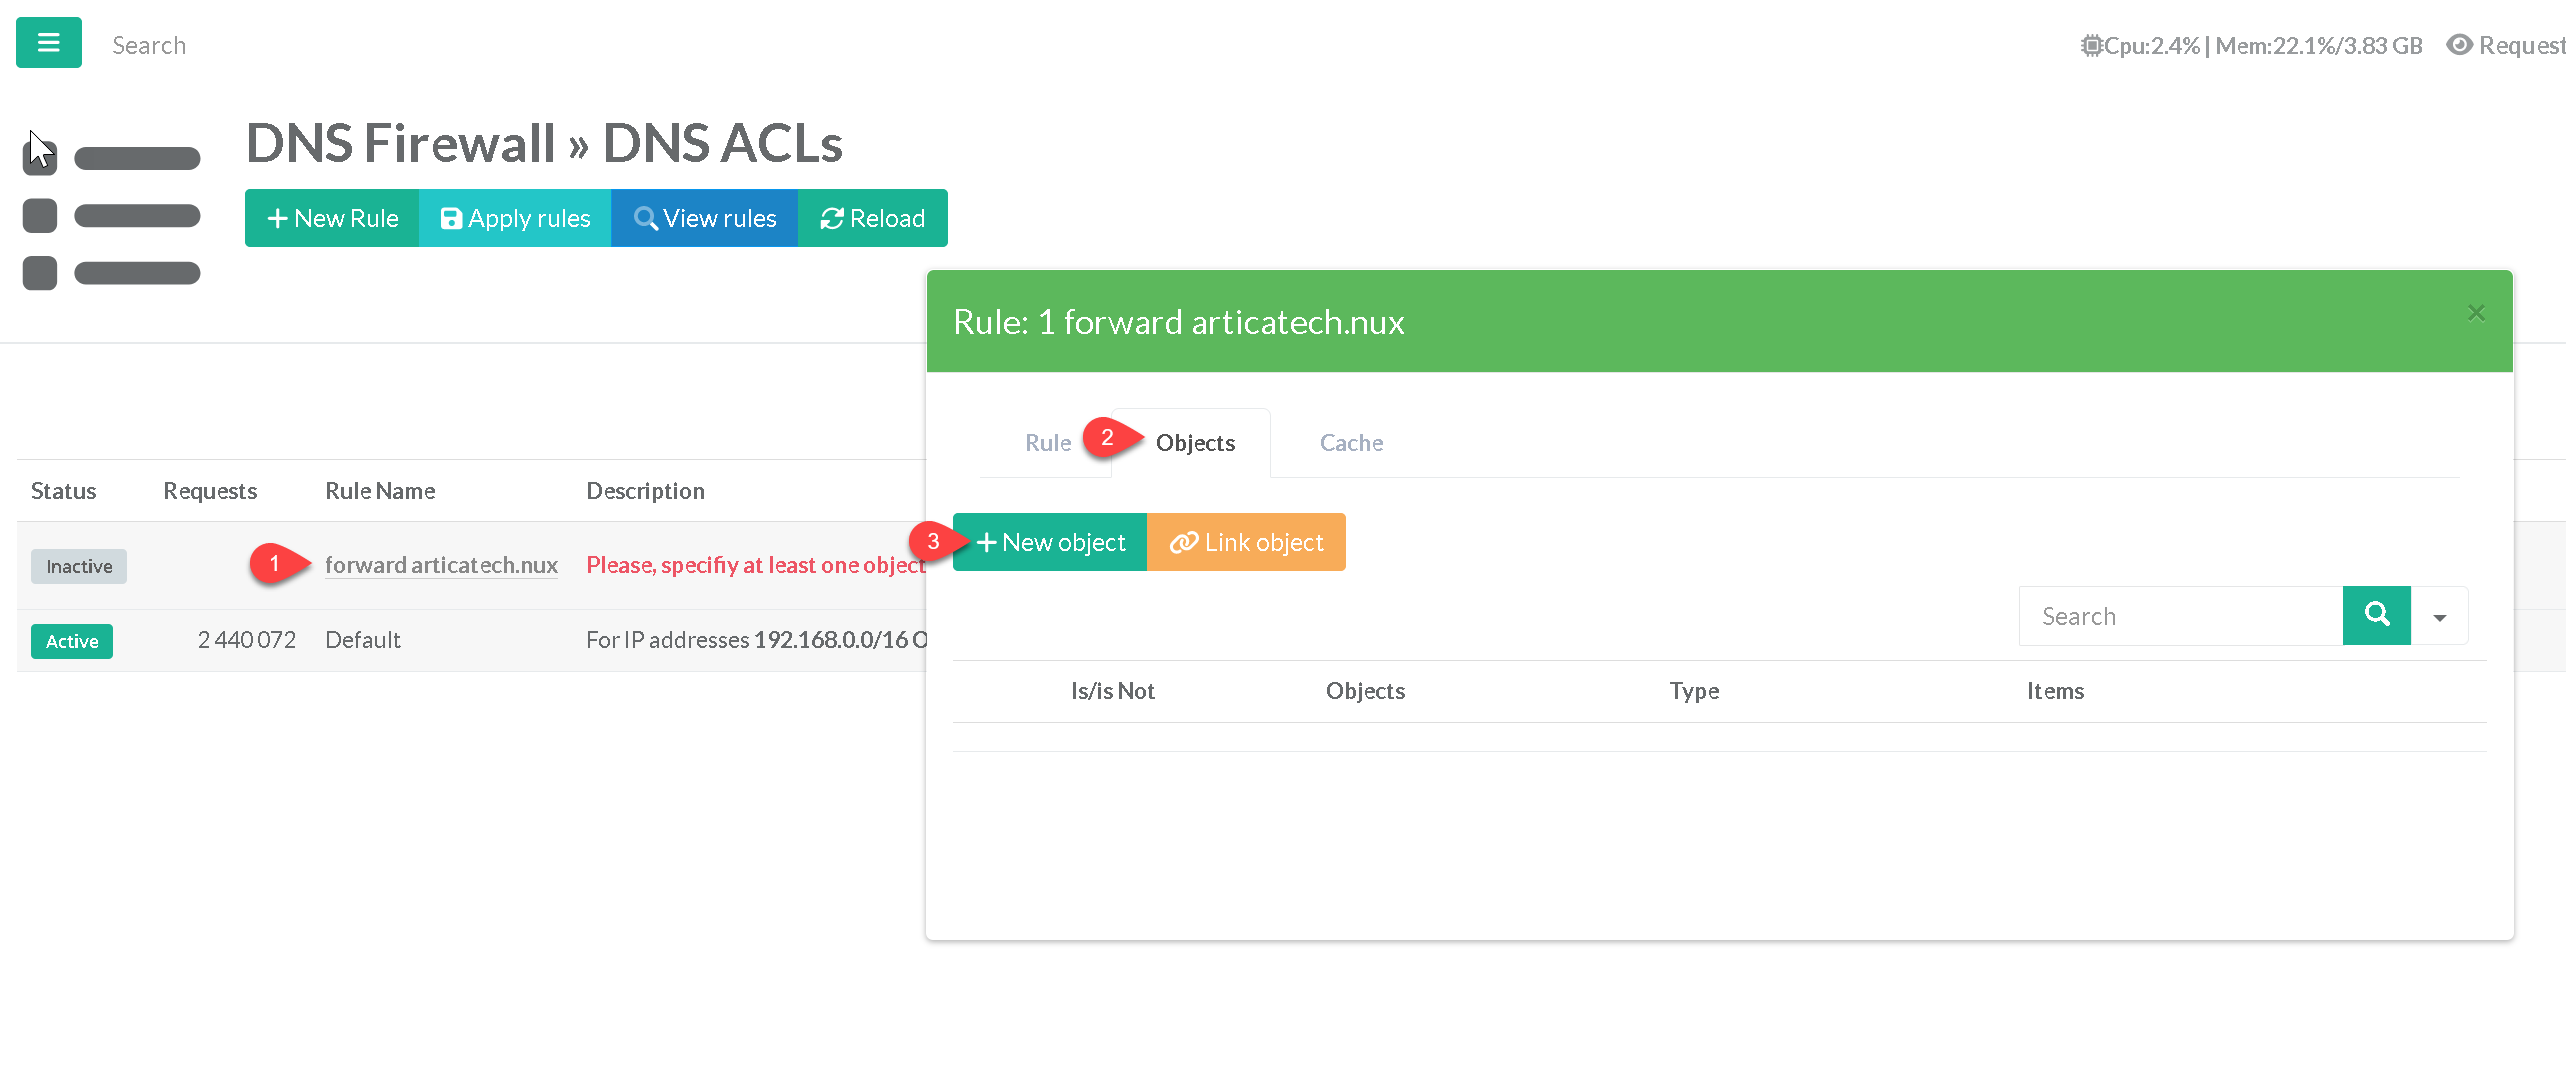
Of course, if you want to reuse previously created objects, use the “Link object” button
- Set the object name and with the choose button, search the
domainword and choose the the “Web server or domain” type. - Click on Add button
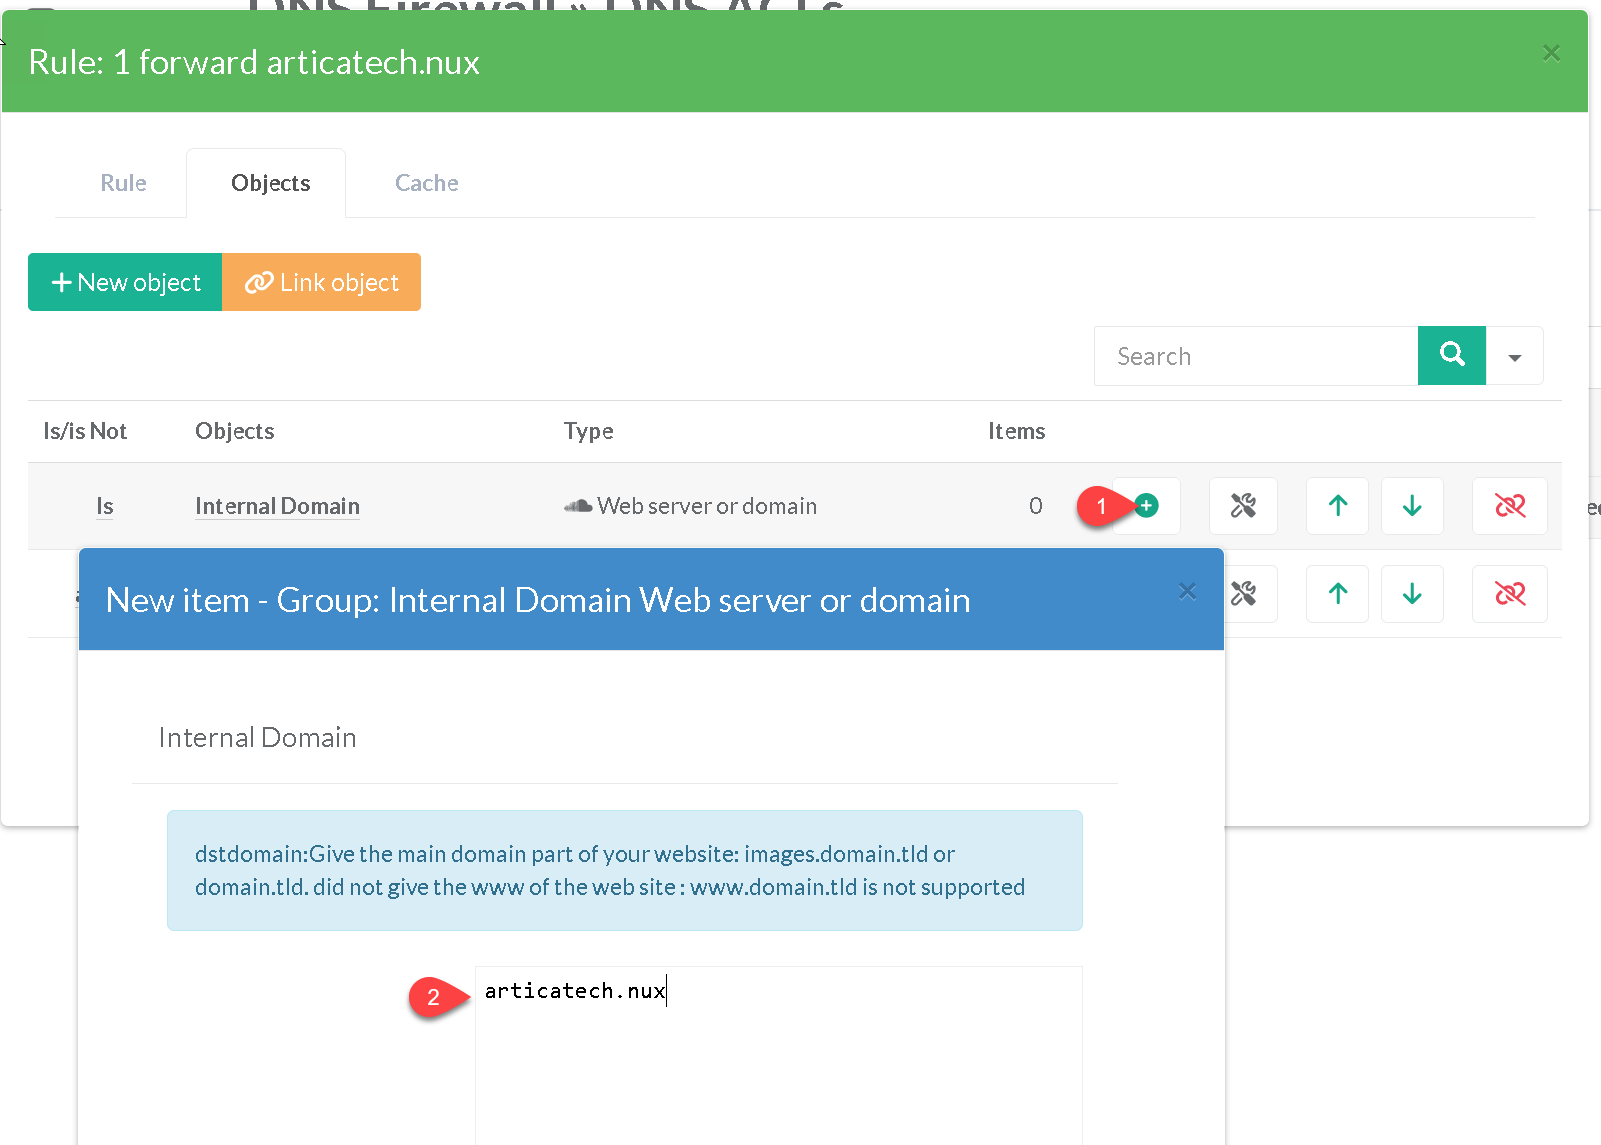
- Click on the “plus” sign and add the domain you want to route
- Click on Add button
C) Create the DNS server address object
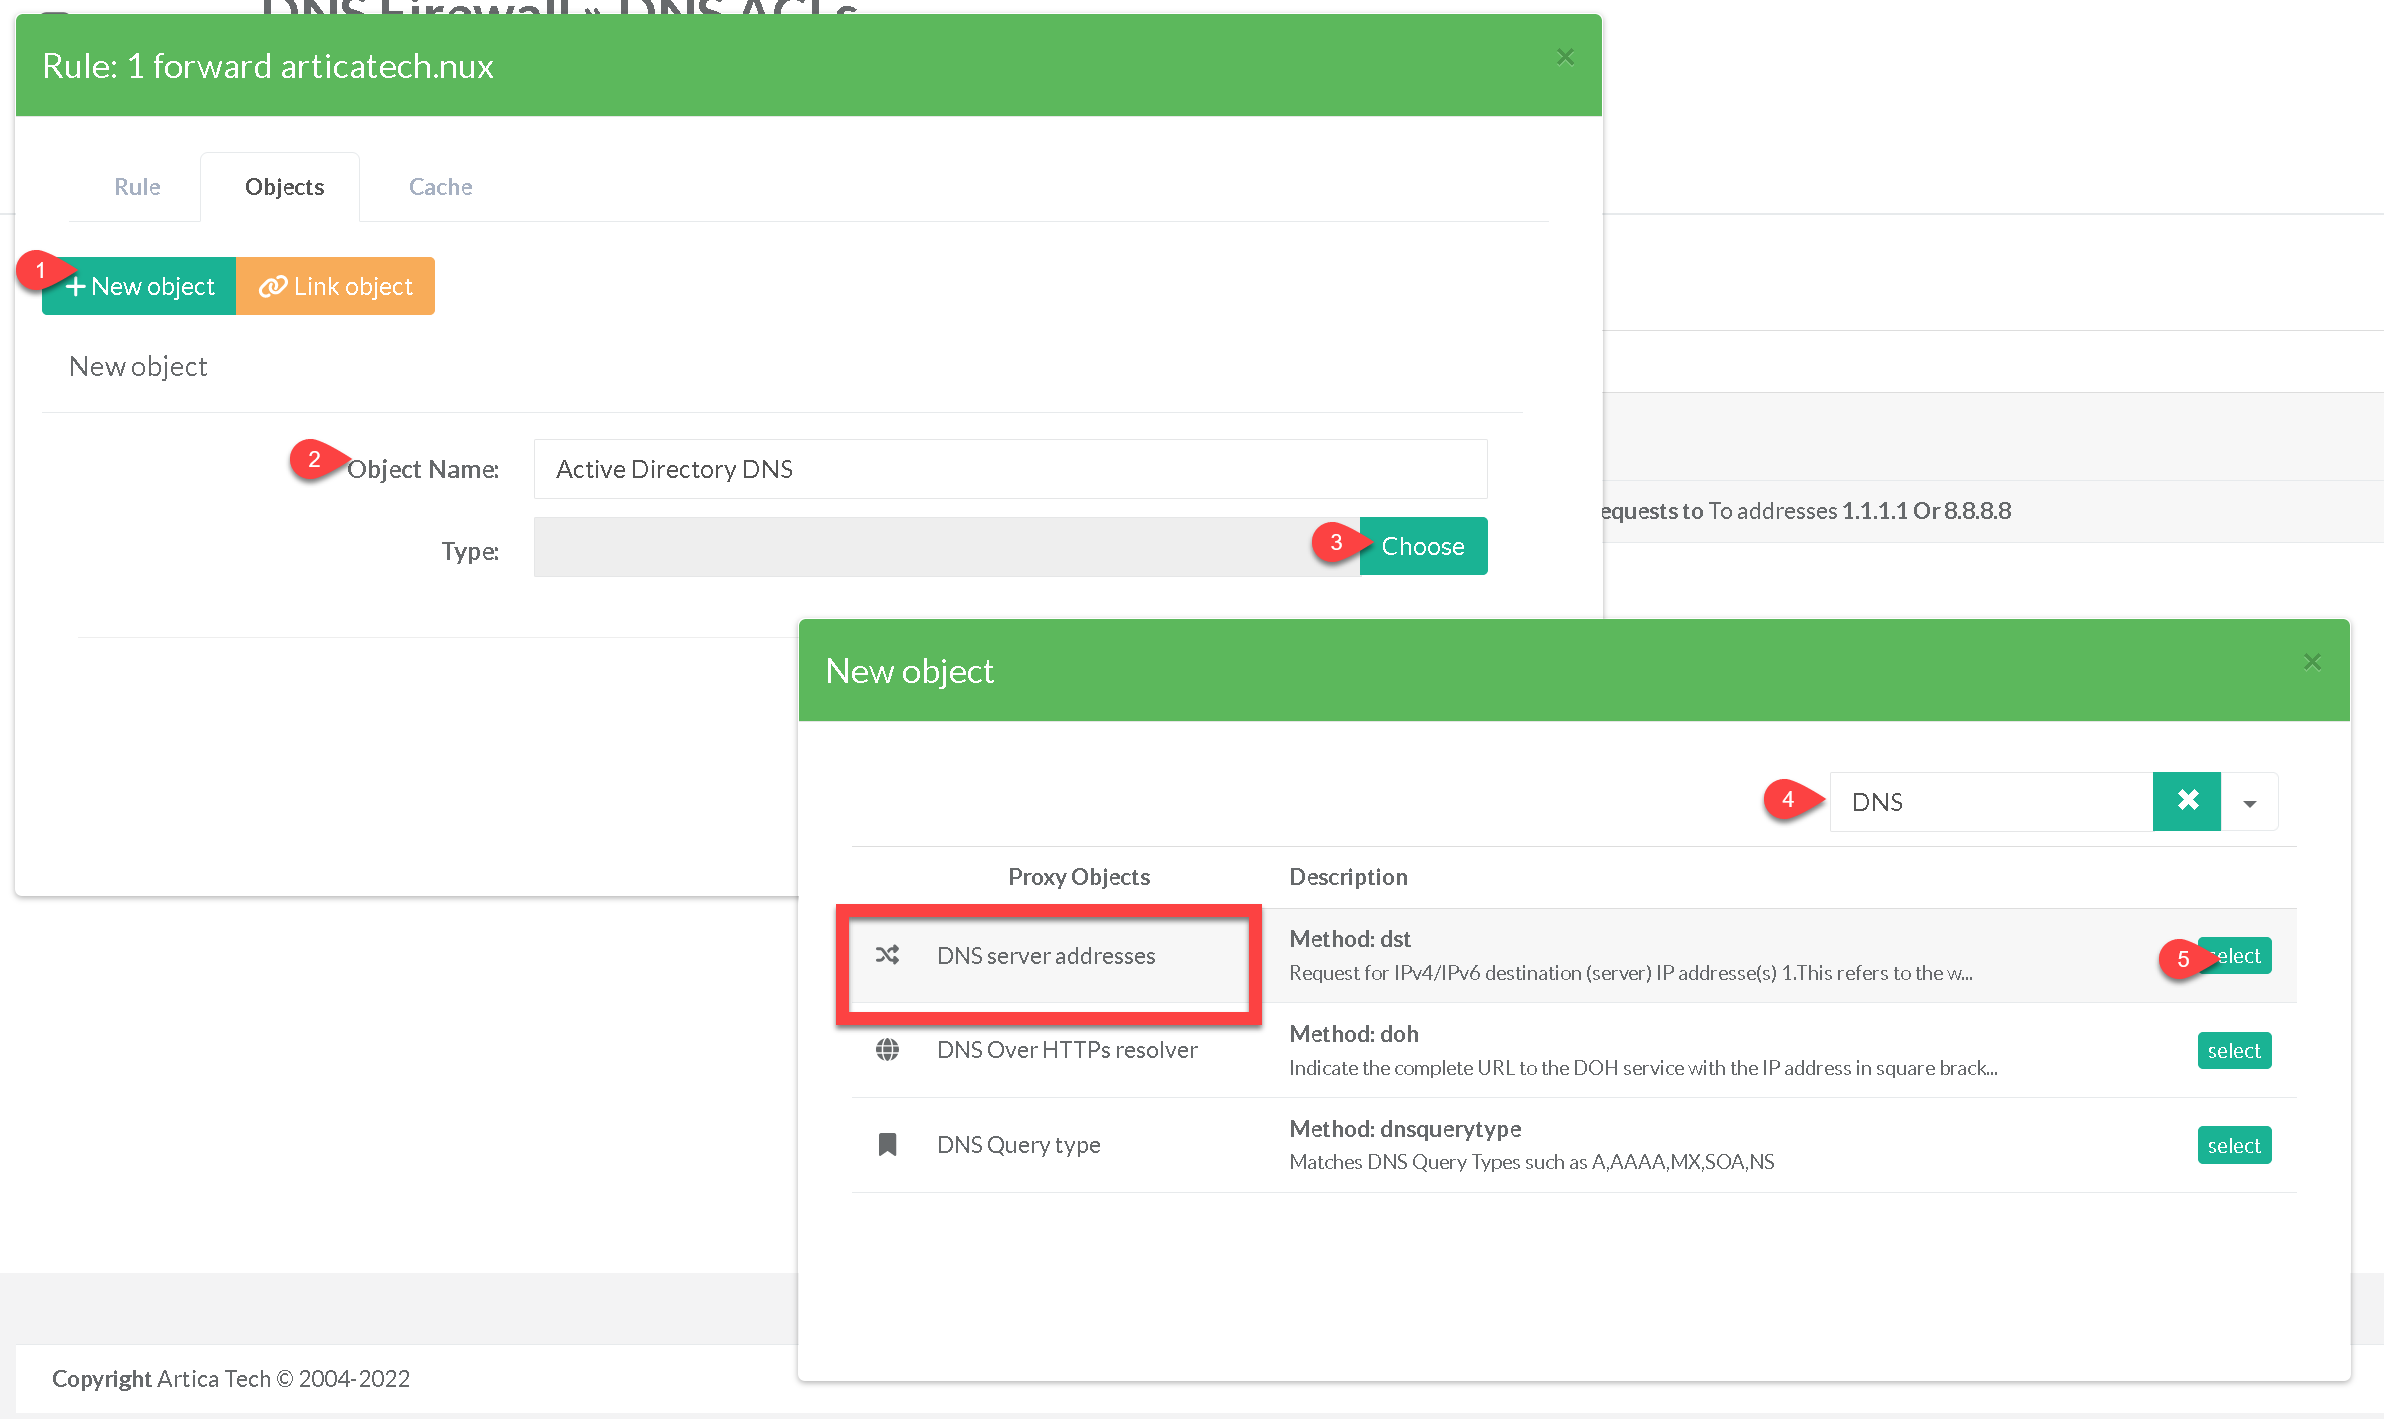
- In the same way, set the object name and with the choose button, search the
DNSword and choose the the “DNS server address” type. - Click on Add button
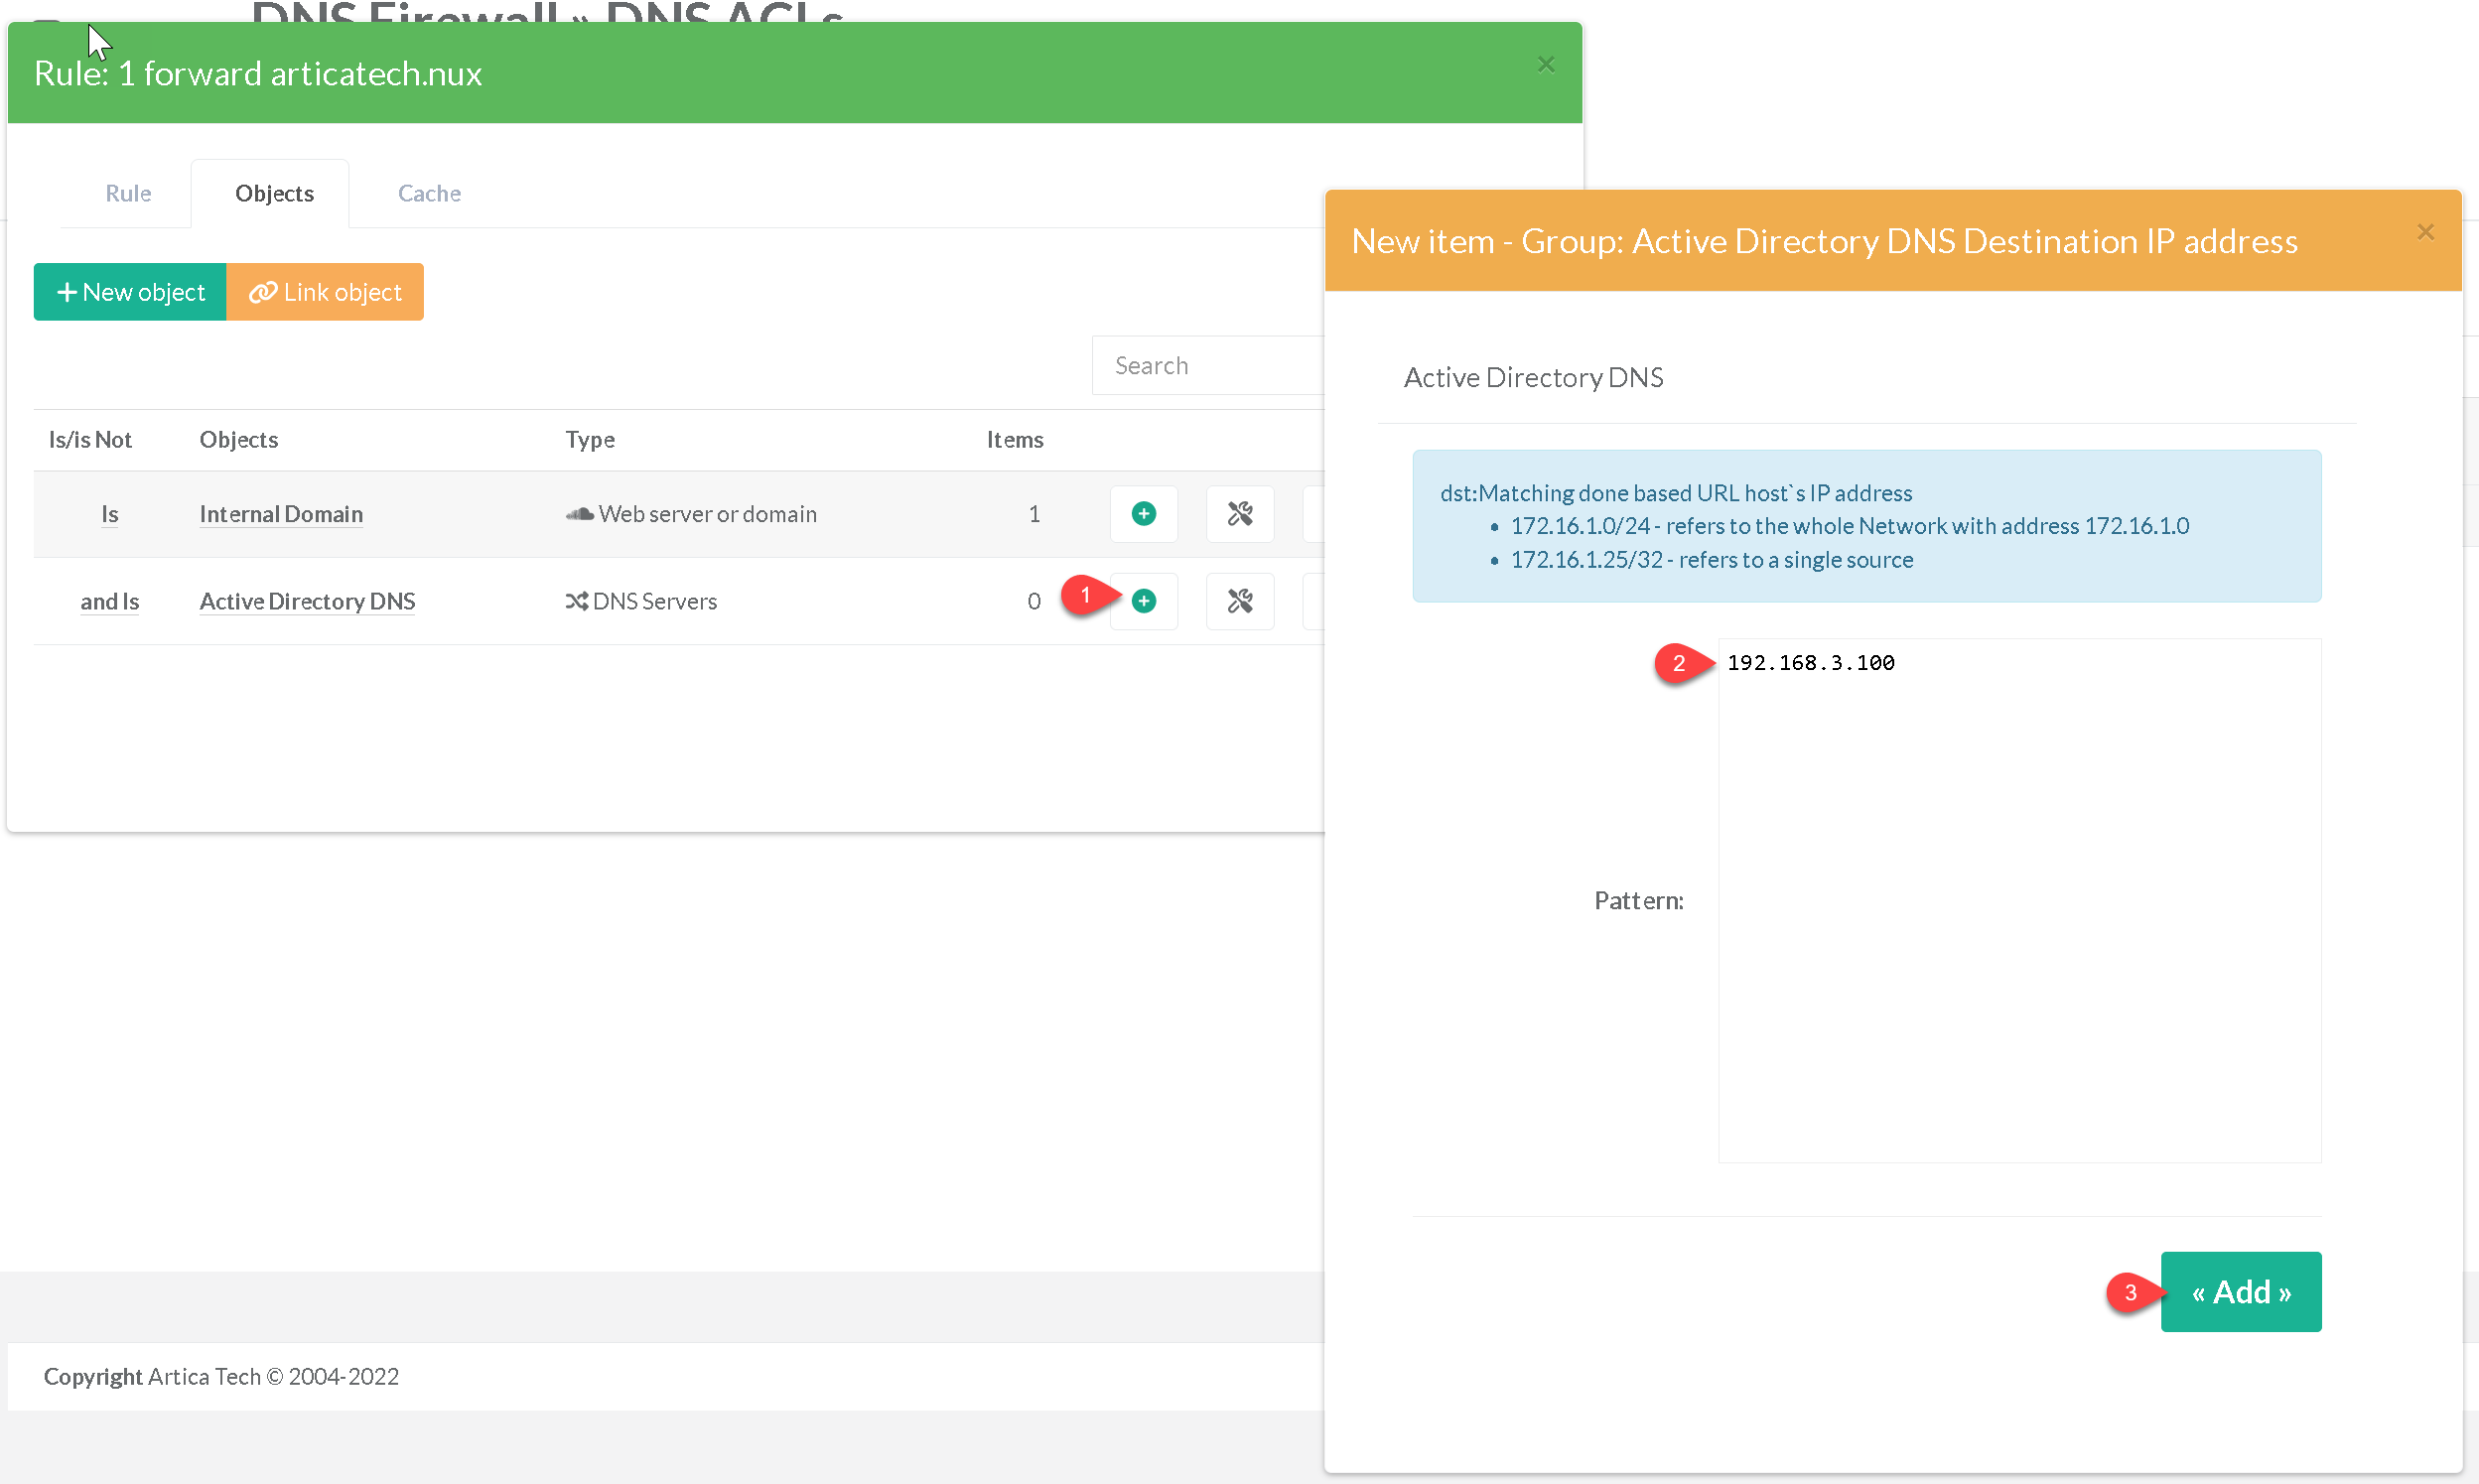
- Click on the plus icon and put the IP address of your targeted DNS server.
- Click on Add and close the rule
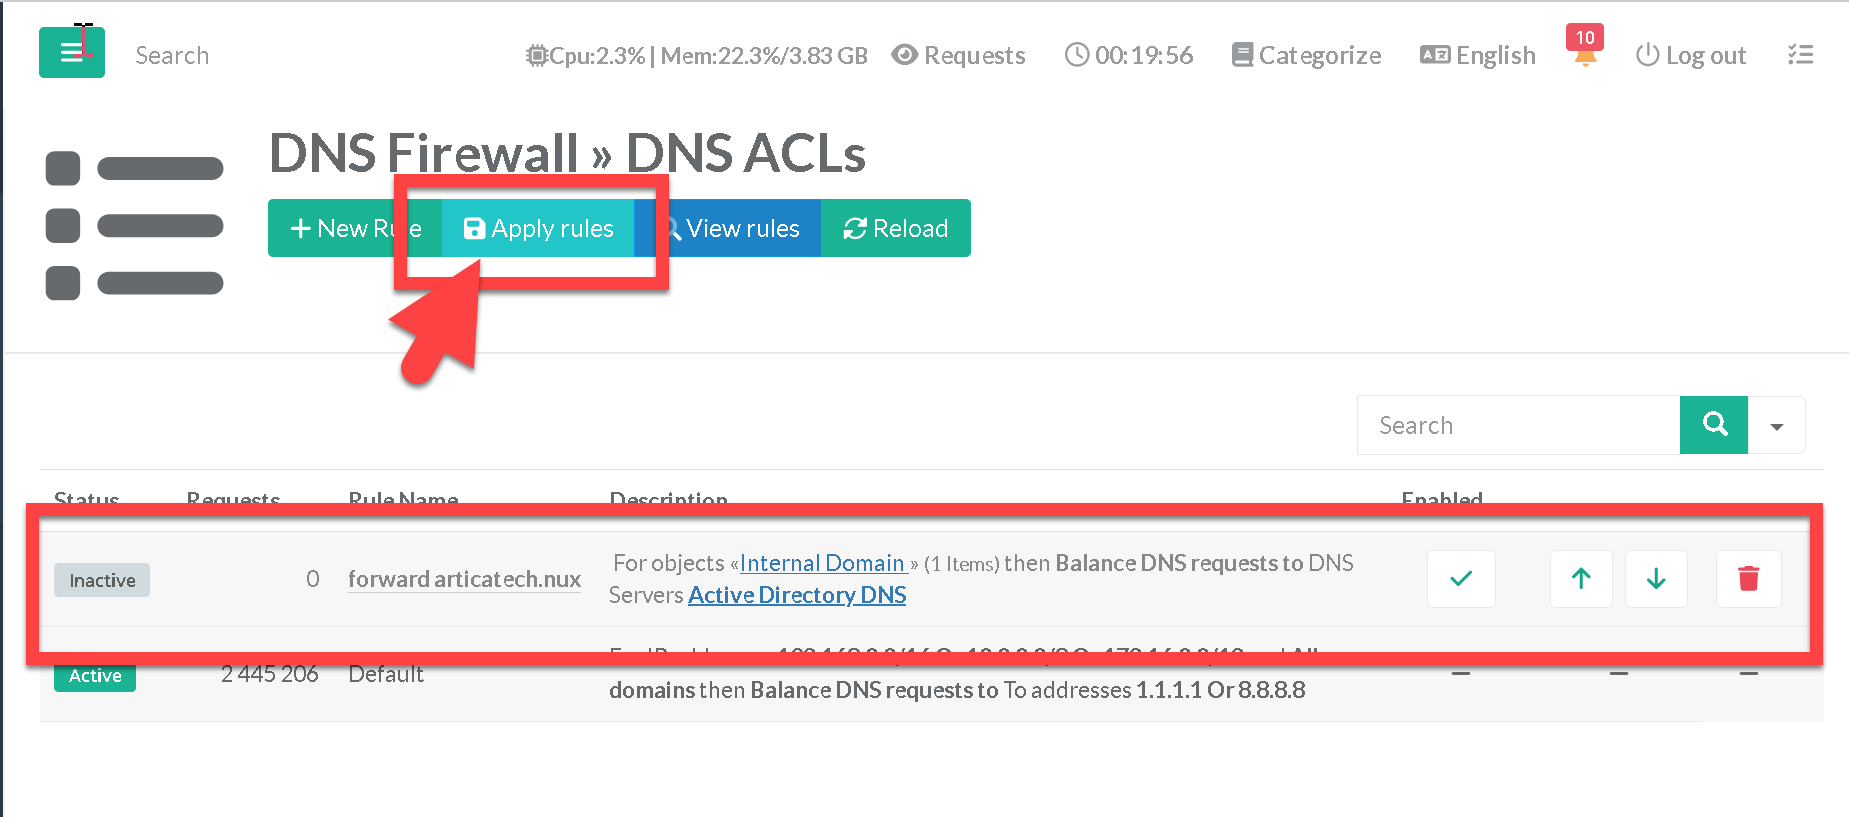
Finally compile your rules
- Your newly created rule is currently inactive, to make it active, you must apply your rules.