Time Synchronization with Active Directory
Time Synchronization with Active Directory is critical when using Kerberos method, you need to ensure that the Active Directory time is the same on the Artica Proxy
To ensure that your Artica proxy is corrently synchronized it is better to enable your Active Directory as NTP time server and then allow Artica to synchronize its time using Your Artica Directory as source clock server.
See “Time synchronization with Active Directory did not working properly”
Turn on the NTP service on your Windows 2019 Active Directory:
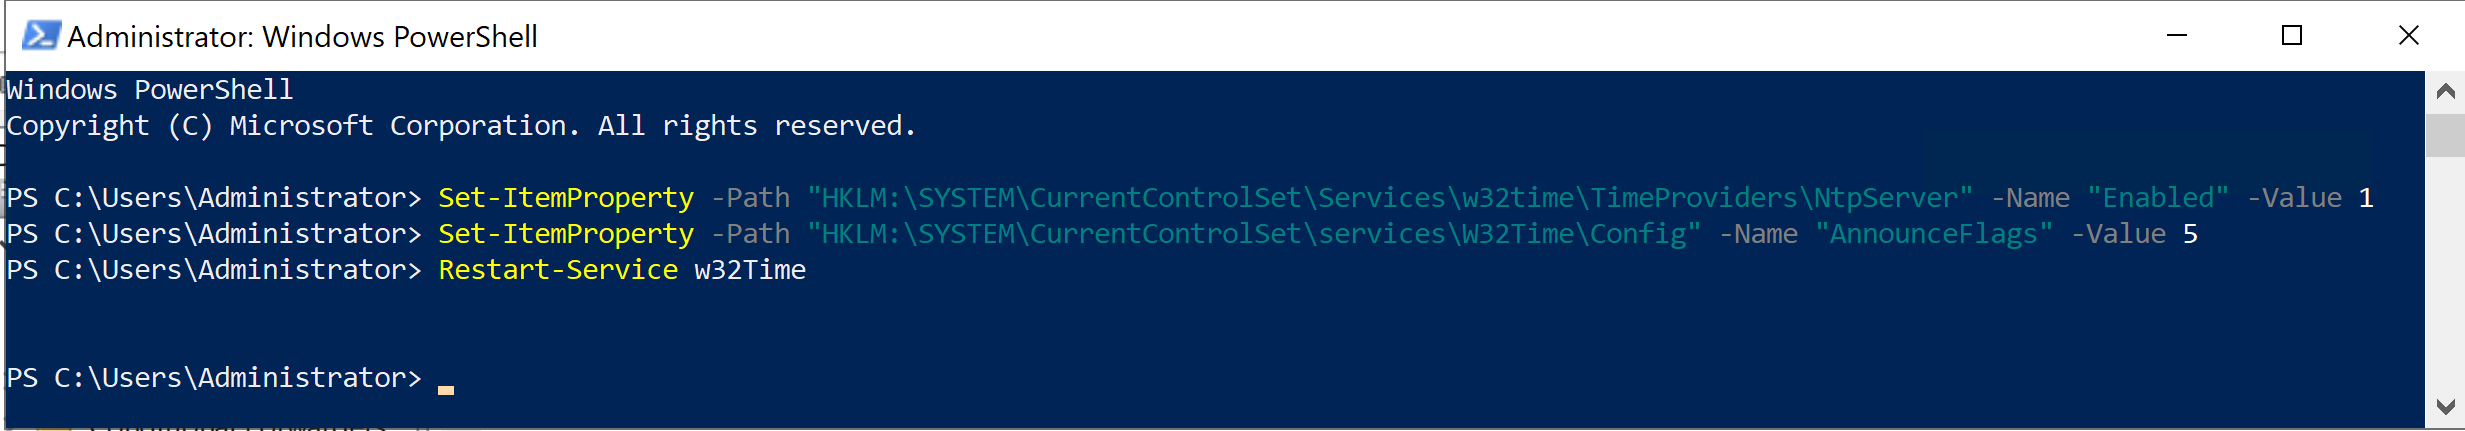
Open a PowerShell console and type the following code:
Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\w32time\TimeProviders\NtpServer" -Name "Enabled" -Value 1
Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\services\W32Time\Config" -Name "AnnounceFlags" -Value 5
Restart-Service w32Time
Connecting Artica with NTP synchronization
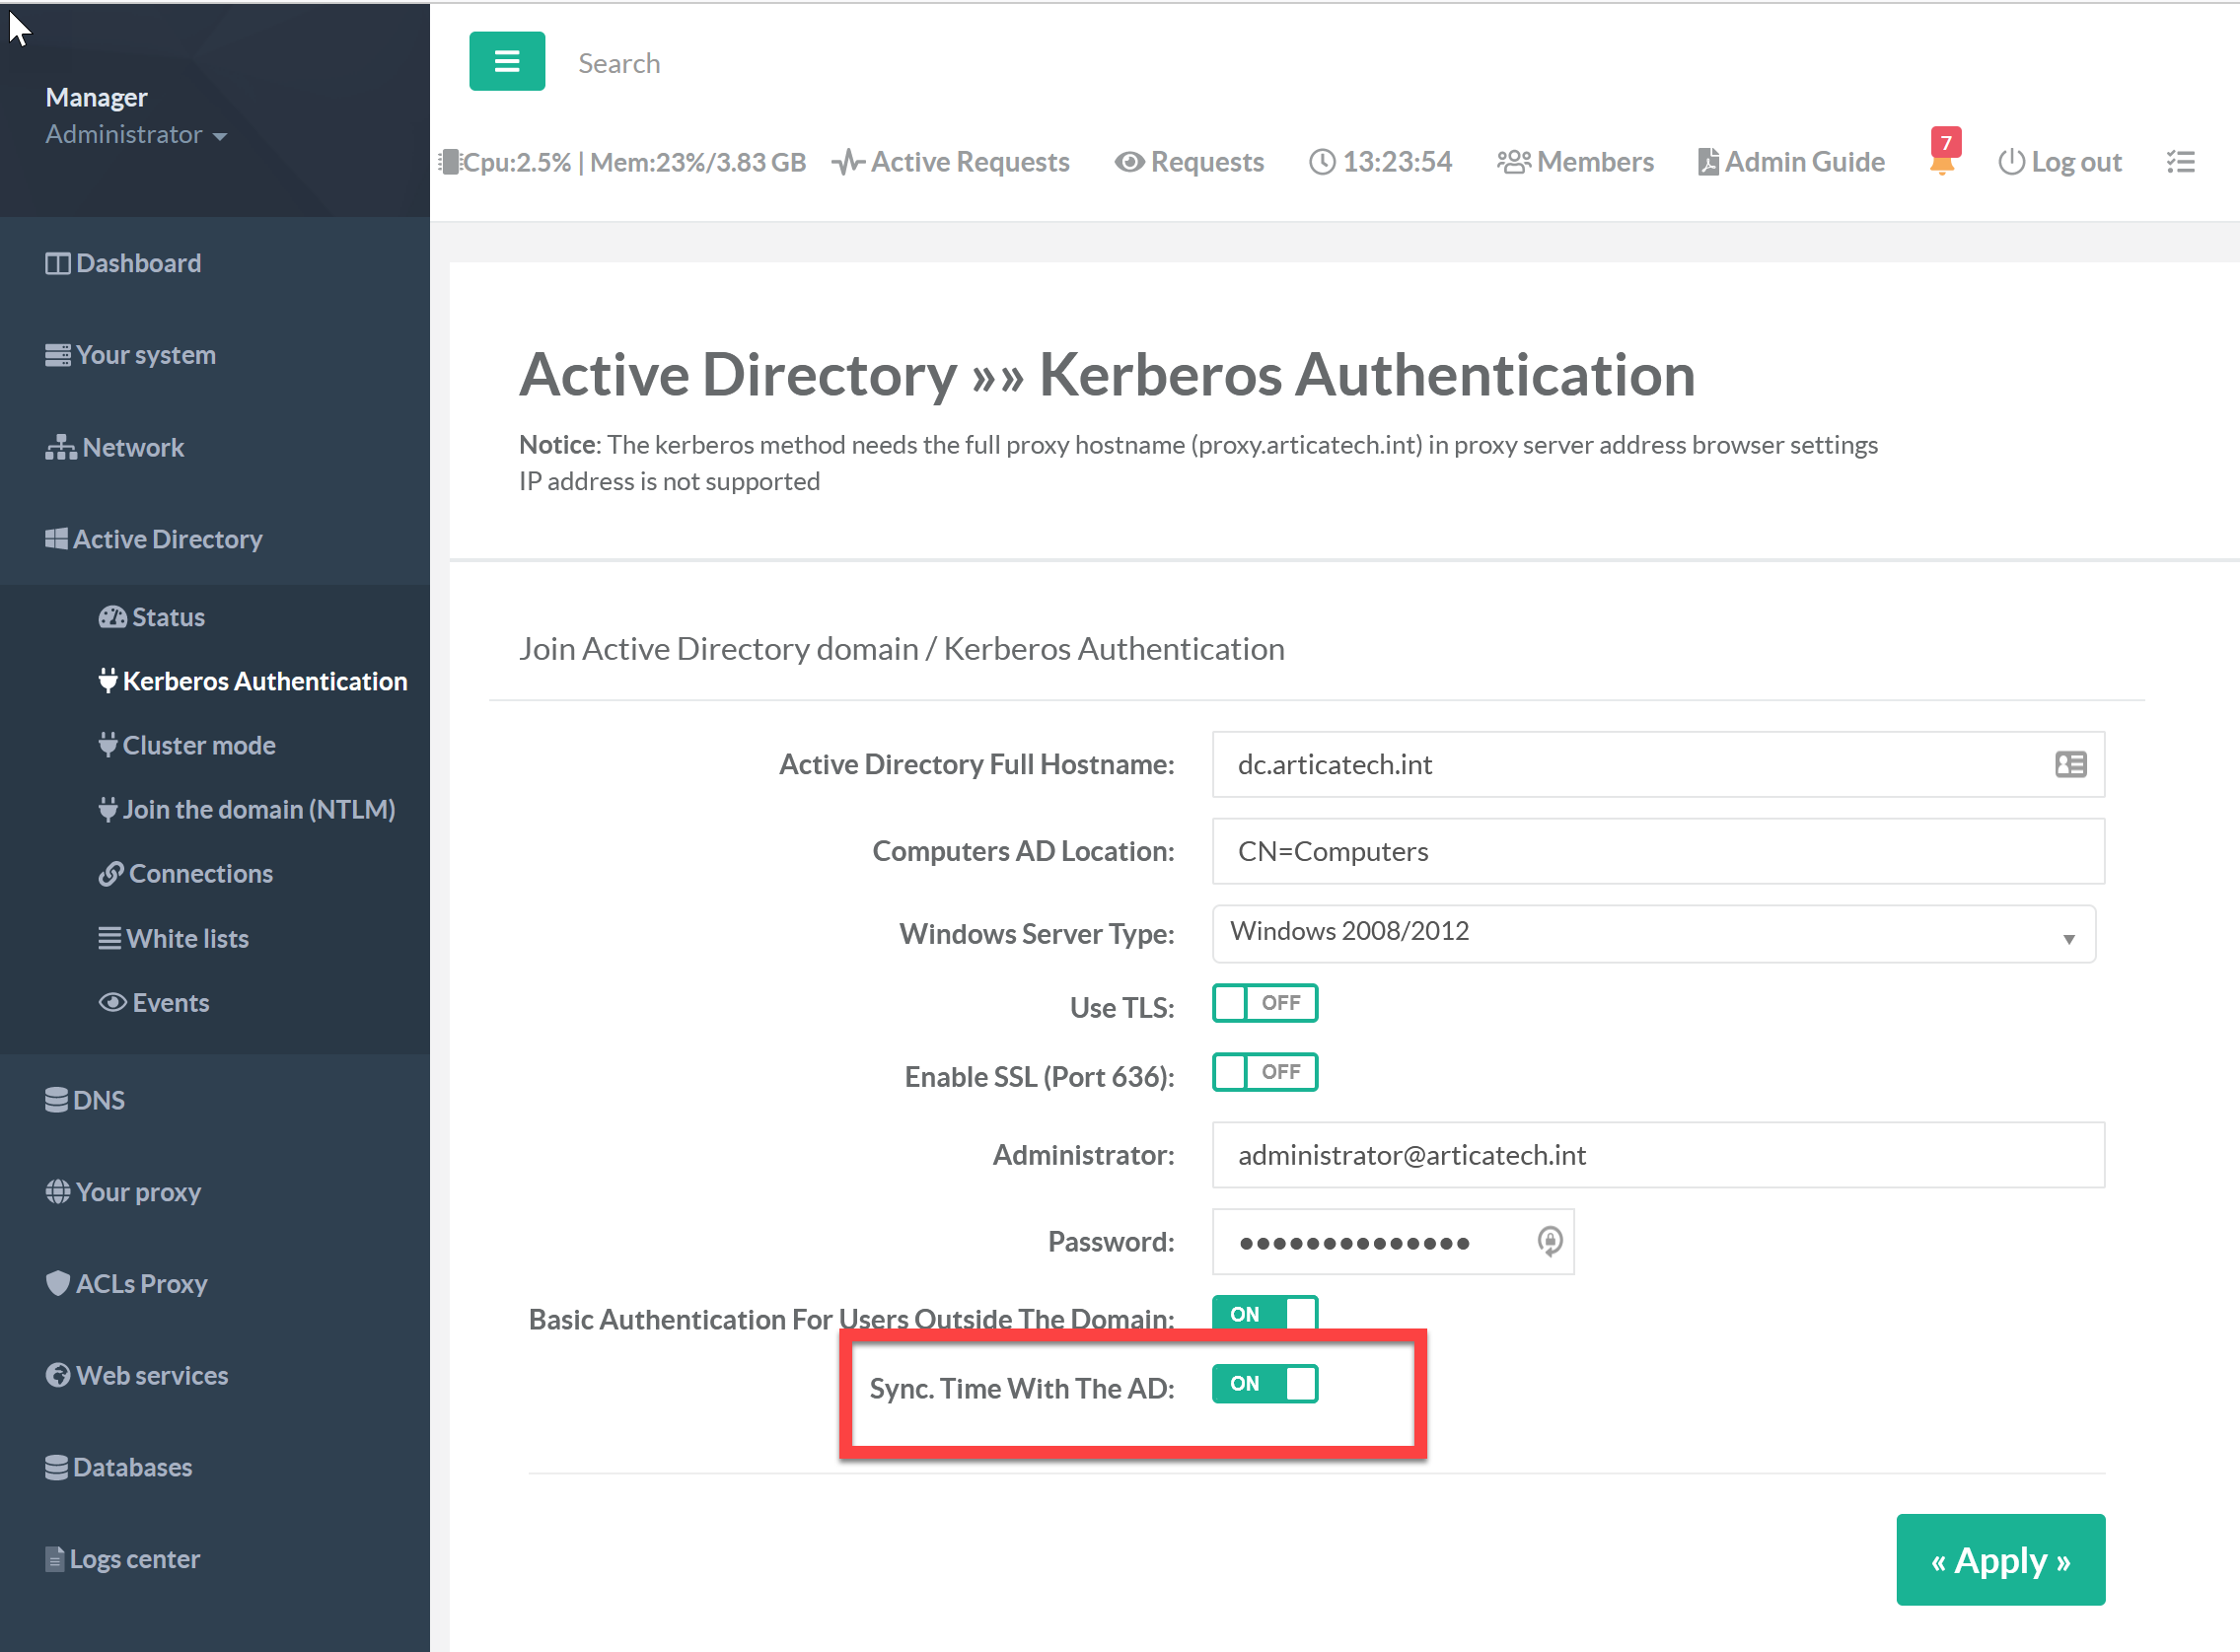
- Before link your Artica server to your domain controller, ensure that the “Sync time with the AD” is turned to ON